A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.
A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.
A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.
Cycling through all six. Tap any point to stop.
Measured on six things
AI governance platform for EU AI Act, ISO 42001, and NIST...
Desktop Lighthouse 96/100 is genuinely quick, but mobile 62/100 with a 7.5s LCP is rough for a B2B tool people check on phones between meetings.
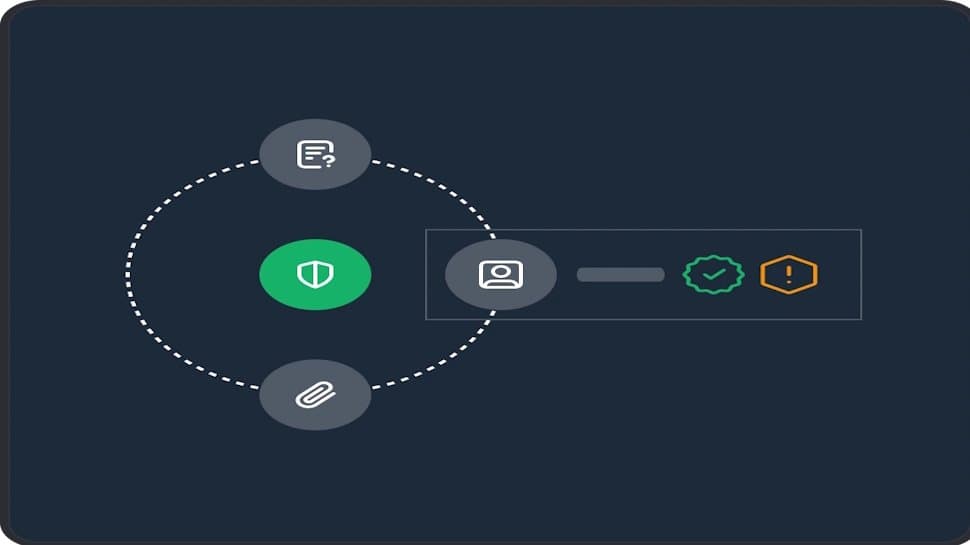
AI Sigil is a purpose-built AI governance platform that helps organizations map their AI systems to regulatory obligations, track controls, and collect evidence to prove compliance. It stands out by offering out-of-the-box support for the EU AI Act (113 articles, 62 controls), ISO 42001 (10 clauses + 38 Annex A controls), and NIST AI RMF (coming soon). Unlike generic GRC tools adapted for AI, AI Sigil is built from AI regulations first, with every control quoting the exact legal text. The platform enables compliance, legal, and AI development teams to collaborate seamlessly, turning governance work into a defensible audit trail. Key features include AI system inventory, risk classification, framework activation, control assessment, evidence collection, and audit-ready documentation. With EU hosting and GDPR compliance, AI Sigil is ideal for organizations deploying AI in regulated environments.
Drawn from the product itself, not from a survey.
Demographic
Compliance and Risk Managers in mid-to-large enterprises
Pain points
Overwhelmed by complex AI regulations, manual tracking in spreadsheets, and difficulty proving compliance to auditors.
Primary needs
Centralized platform to map AI systems to regulations, automate control tracking, and generate audit-ready evidence.
Demographic
Legal Teams in tech companies using AI
Pain points
Struggling to interpret and apply evolving AI laws, ensure legal basis for decisions, and collaborate with technical teams.
Primary needs
Clear linkage between controls and legal text, documentation of regulatory basis, and streamlined communication with compliance and AI teams.
Demographic
AI Development Leads in regulated industries (e.g., healthcare, finance)
Pain points
Building AI systems without clear governance guidance, fear of non-compliance, and time lost on manual documentation.
Primary needs
Easy registration of AI systems, automated risk classification, and integration of compliance into development workflows.
Written by AI from measured evidence, scored out of 100.
AI Sigil is a purpose-built AI governance platform for teams staring down the EU AI Act and ISO 42001. The pitch is sharp: every control quotes the exact legal text, provider and deployer roles are distinguished, and content adapts to risk classification. Pricing is refreshingly simple — 999€/month for up to 25 AI systems with unlimited seats, or custom Enterprise with SSO, custom retention and a named contact. The security posture is the standout: 12/12 headers, HSTS, CSP, DMARC, EU hosting, and DPA/MSA/security questionnaire bundled rather than upsold. The gaps are honest ones for an early-stage product: mobile performance lags desktop badly, accessibility has real failures with no published statement, and two of three advertised frameworks are still 'Coming Soon'. The core idea — regulation-first governance instead of GRC-with-an-AI-tab — is the right one for a market that's about to get loud.
Two clear plans, 14-day trial, self-service Core onboarding, and no per-seat fees. Five nav dropdowns and dense framework cards add friction for first-timers.
Clean hero, consistent red accent, and a readable dashboard mockup. But two of three framework cards show 'Coming Soon' on the live homepage, and the system cards are tag soup.
Desktop Lighthouse 96/100 is genuinely quick, but mobile 62/100 with a 7.5s LCP is rough for a B2B tool people check on phones between meetings.
12/12 security headers, HSTS, CSP, DMARC, EU hosting and GDPR claims, plus DPA/MSA/security questionnaire bundled on Enterprise. No public SOC 2 or ISO cert verified.
Lighthouse a11y 88/100 with real misses: contrast failures, broken heading order, non-focusable skip links, no main landmark. No WCAG statement published.
Real, dated problem (EU AI Act, ISO 42001) with verbatim legal text and flat 999€ pricing vs per-seat GRC incumbents. NIST still 'Coming Soon' limits the wedge.
AI Sigil's homepage is competent rather than striking: a bold hero, a consistent red accent, and a dashboard mockup that reads like a real inventory view. The problem is the framework section, where ISO 42001 and NIST AI RMF both sit behind gray 'Coming Soon' buttons on a page that leads with 'out of the box'. Usability is stronger: two plans (Core 999€/month up to 25 systems, Enterprise on demand), unlimited seats on both, a 14-day trial, and self-service onboarding on Core. Five nav dropdowns and tightly packed framework cards make the first visit busier than it needs to be, and SSO/SAML plus custom audit log retention are Enterprise-only. For a compliance buyer who lives in this tool daily, the workflow density is a feature; for a first-time evaluator, it's a lot of clicking before value.
Speed is split down the middle. Desktop Lighthouse lands at 96/100, which is genuinely fast, but mobile sits at 62/100 with a 7.5-second LCP and 3.8s FCP — the kind of number that shows up when a compliance manager opens the audit trail on a phone. CLS is 0 and TBT is 181ms, so the layout is stable; it's the initial paint that drags. Security is the strongest dimension on paper: the HTTP probe returned 12/12 checklist points including enforced HTTPS, HSTS, CSP, frame protection, Referrer-Policy, Permissions-Policy, SPF and DMARC. The pricing page states DPA, MSA, vendor security questionnaire and SOC reports are bundled on Enterprise rather than sold as add-ons, and the site claims EU hosting with GDPR compliance. What's missing is the public artifact — no downloadable SOC 2 report, no ISO certification page, no bug bounty. For a governance vendor, publishing the audit trail you sell would be the sharpest possible proof.
Accessibility is the weakest measured dimension: Lighthouse 88/100 with concrete failures — insufficient color contrast, non-sequential heading order, non-focusable skip links, no main landmark, and ARIA roles missing required children. There's no accessibility statement or WCAG conformance claim anywhere on the site, and no multi-language support mentioned, which is notable for a product selling EU AI Act compliance to EU enterprises. Growth is a different story. The problem is real and dated: the EU AI Act has 113 articles and organizations are tracking them in spreadsheets. AI Sigil's wedge is regulation-first design — every control quotes the legal text verbatim, with 62 EU AI Act controls and ISO 42001's 10 clauses plus 38 Annex A controls mapped. Against Vanta and OneTrust, which are generic GRC platforms with AI modules bolted on, that specificity matters. The flat 999€/month with unlimited seats is a genuine counter to per-seat pricing. The limit is coverage: NIST AI RMF is still 'Coming Soon', and the buyer is a compliance manager who already has a GRC vendor relationship. The wedge is real but narrow until the framework library fills out.
Conclusion
If you're a compliance or legal lead at a mid-to-large enterprise and your AI inventory currently lives in a 47-tab spreadsheet, AI Sigil is worth the 14-day trial — the verbatim legal text on every control is the feature that will actually save you time with auditors. Go in with clear eyes: you're buying EU AI Act and ISO 42001 coverage today, not NIST, and you'll want to test the mobile experience and run your own accessibility check before rolling it out to a broad team. The flat pricing and unlimited seats make it easy to pilot without a procurement fight. The product is early, but the positioning is right, and the security fundamentals are in place. For a governance tool, that's a defensible starting point.
Named competitors, point by point. Nobody paid to appear here or to be left out.
 AI Sigil |  Vanta |  OneTrust | |
|---|---|---|---|
| Primary focus | Purpose-built AI governance: EU AI Act and ISO 42001 mapped from the regulation text first. | Generic GRC automation for SOC 2, ISO 27001, HIPAA, with AI governance features added on. | Privacy and compliance management platform with AI governance modules, not AI-regulation-first. |
| EU AI Act coverage | 113 articles mapped to 62 controls, verbatim legal text, provider/deployer roles, risk-classification-aware. | AI governance features available but not a full article-by-article EU AI Act control library. | AI governance module covers regulatory mapping but is not built from the AI Act text first. |
| ISO 42001 support | 10 clauses plus 38 Annex A controls mapped, listed as 'Coming Soon' on the live homepage. | ISO 27001 and other standards supported; ISO 42001 coverage is part of the broader GRC framework set. | Framework library includes ISO standards; AI-specific ISO 42001 depth varies by module. |
| Pricing model | Flat 999€/month Core (up to 25 AI systems, unlimited seats); Enterprise custom. No per-seat or per-framework fees. | Quote-based pricing typically scaled by frameworks and company size; no public flat rate. | Enterprise quote-based pricing across privacy, GRC and AI modules; no public flat rate. |
| SSO / SAML | Enterprise plan only; Core plan does not include SSO/SAML. | SSO typically available on higher tiers of the GRC platform. | SSO/SAML standard across enterprise deployments. |
| Target customer | Compliance, legal and AI development teams in mid-to-large enterprises deploying AI in regulated environments. | Startups and mid-market companies seeking SOC 2, ISO 27001 and broader compliance automation. | Large enterprises needing integrated privacy, consent and governance across multiple domains. |
Vanta
A generic GRC platform that offers compliance automation for standards like SOC 2, ISO 27001, and HIPAA, with some AI governance features added.
OneTrust
A privacy and compliance management platform that includes AI governance modules, but is not exclusively built for AI regulations.
Comparing options? See AI Sigil alternatives, scored side by side

Privacy-first open source journal app with a continuous t...

A free, open-source platform offering 110 AI agent skills...

An all-in-one hospitality software for restaurants and ba...

All-in-one AI workspace for docs, projects, and knowledge...

White-label reputation management software for agencies s...

A weekly newsletter delivering curated tech jobs, intervi...

Puzzly is an all-in-one B2B lead generation platform that...

Open-source desktop app for switching AI coding providers...

One verified handle for your online identity, readable by...

Frame-perfect video-to-GIF maker that runs entirely in yo...

White-label website audits that close deals for digital a...

PERM Processing Time is an independent data analysis platform that helps users navigate the U.S. Department of Labor’s permanent labor certification process.
A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.
