Cycling through all six. Tap any point to stop.
Measured on six things
Built with Lovable, Supabase, Base44, or Bolt? Decloak scans your app for the security issues AI builders consistently skip, starting with the #1 vibe-coder failure: a Supabase database left publicly readable because Row Level Security was never turned on. It auto-detects your platform, checks 8 layers including exposed API keys and leaked service_role keys, and returns a graded report in 15 seconds. Free, no account or card required.
Growth
28Extremely early-stage product (domain June 2026) with zero external traction, reviews, or community signals despite live free tier and content updates.
Screenshots
1 / 4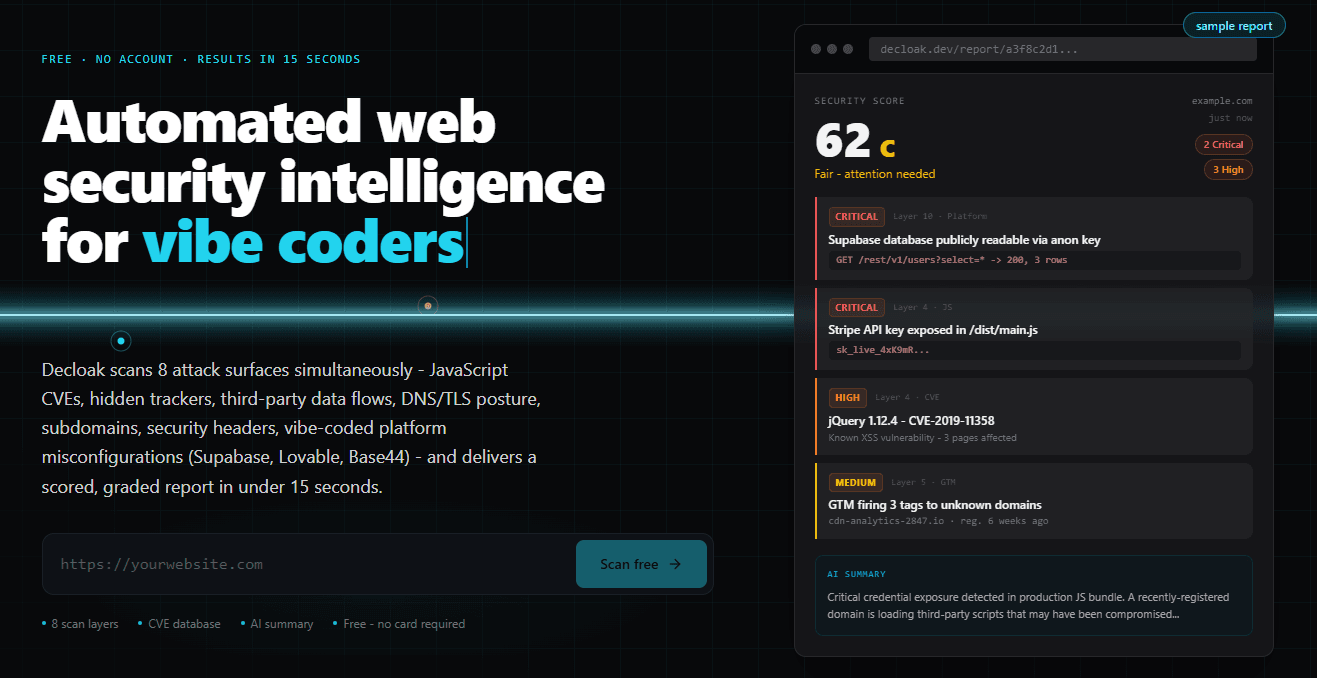
About this app
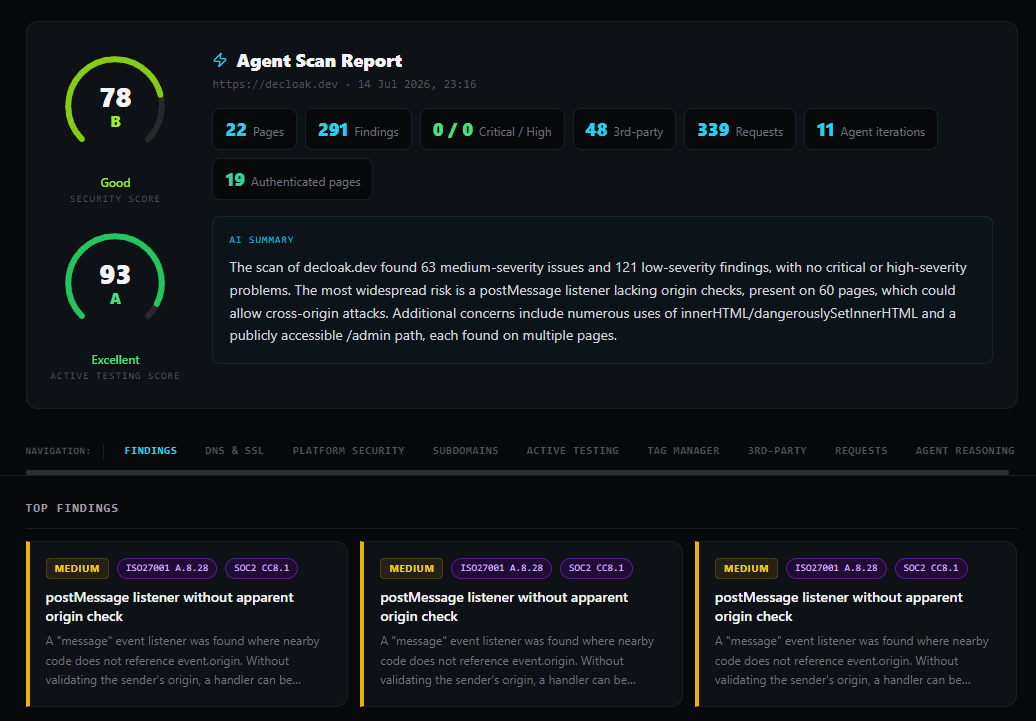
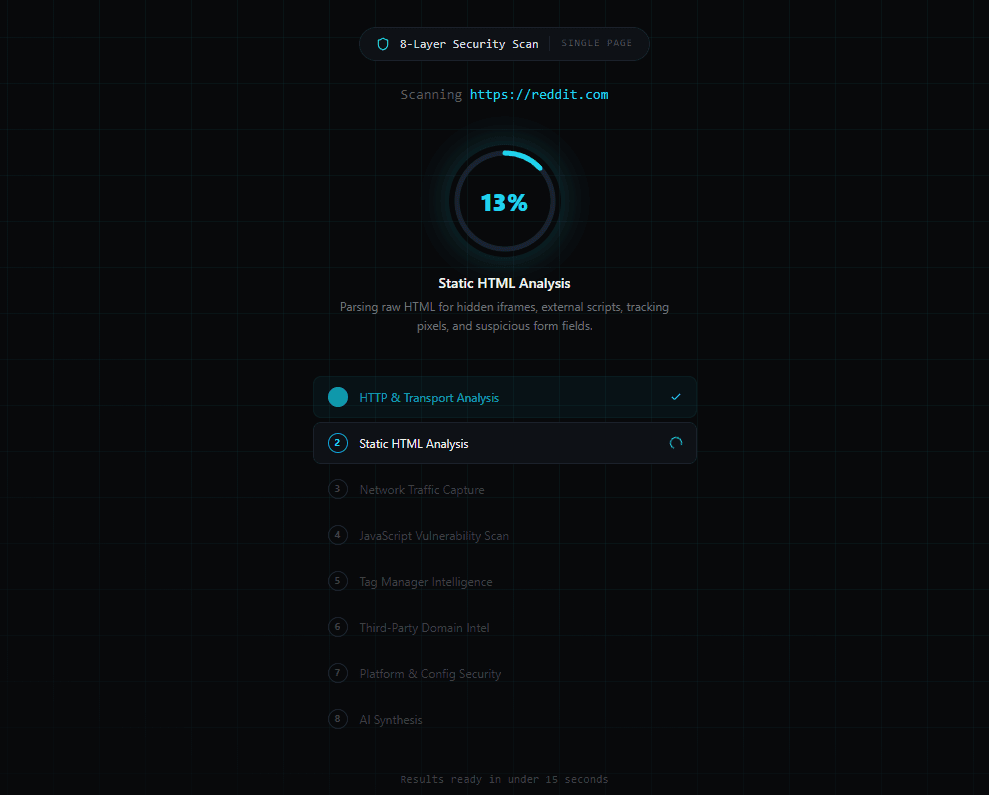
Vibe coding gets you from idea to live app in hours, but the security review is usually the first thing that gets skipped. Decloak is built to catch what shipping fast leaves behind. Paste your URL and Decloak automatically fingerprints your platform - Lovable, Supabase, Base44, Bubble, or Next.js - then checks for the specific misconfigurations known to affect each one. The most common failure it catches: a Supabase database left publicly readable because Row Level Security was never enabled, meaning anyone can read your data using your own public API key. It also flags leaked Supabase service_role keys sitting in client-side JavaScript, exposed Stripe and other API keys in production bundles, and known platform CVEs like the Next.js middleware authorization bypass. Every scan runs a full 8-layer analysis: HTTP/TLS, HTML, live network traffic, JavaScript CVEs, tag managers, third-party supply chain, platform misconfigurations, and AI synthesis, producing a weighted security score and A-F grade you can track over time. The free tier needs no account or card and returns results with an AI-written executive summary in 15 seconds. Most solo builders never need more than that. If you start shipping client work or need scheduled scans, PDF exports, compliance mapping, or MCP/API access for agent-triggered scans, paid tiers cover that, but the free tier is the whole pitch for solo builders.
Key features
- 1Free no-account scan of 8 attack surfaces with AI summary in <15s, including Supabase/Lovable platform checks.
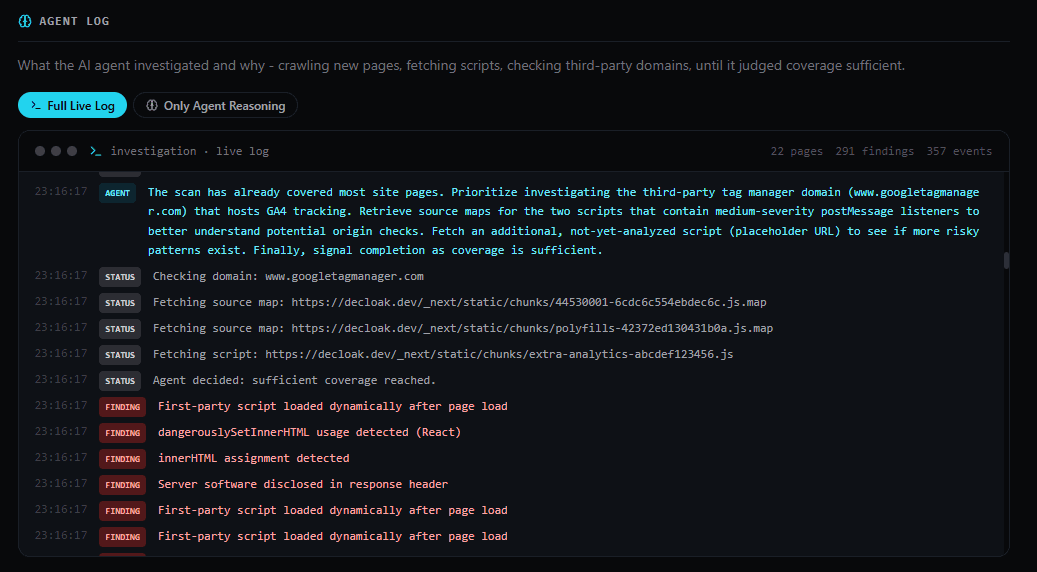
- 2Full AI agent investigation, scheduled scans, PDF exports, and SOC2/ISO control mapping on paid tiers.
- 3Enterprise DAST with authenticated scanning and independent Active Testing Score.
Target customer profile
Drawn from the product itself, not from a survey.
Demographic
Vibe coders and solo builders using AI app builders (Lovable, Supabase, Base44)
Pain points
Shipped fast with AI but skipped security review; exposed API keys and misconfigured databases; no easy way to audit
Primary needs
Quick, free scan to find critical vulnerabilities; platform-specific checks; no login required
Demographic
Small and growing businesses with limited security budgets
Pain points
Can't afford enterprise scanners; need scheduled scans and compliance evidence; worried about forgotten subdomains and misconfigurations
Primary needs
Affordable recurring security audits; DNS/TLS checks; subdomain discovery; easy-to-understand reports
Demographic
Compliance and security teams managing SOC2 or ISO 27001 audits
Pain points
Expensive legacy scanners (Qualys, Tenable); manual mapping to controls; need audit-ready evidence and remediation tracking
Primary needs
Automated control mapping; scheduled scans; PDF evidence packages; multi-domain dashboard; activity logs
Demographic
Agencies and MSPs managing multiple client domains
Pain points
No central security view across clients; manual per-domain checks; need team collaboration and reporting
Primary needs
Unified dashboard; subdomain discovery; team seats; scheduled scanning; shareable reports
Scout Review
Written by AI from measured evidence, scored out of 100.
Decloak.dev is a promising early-stage web security scanner tailored for AI-app builders and small teams who need fast, affordable checks for exposed secrets, missing headers, CVEs, and platform misconfigurations like Supabase RLS failures. Strengths include instant free scans, strong measured performance, and targeted features that larger tools overlook. Weaknesses center on unverified compliance claims and minimal external validation. It positions itself as a lighter, cheaper alternative to AppCheck, Qualys, and Tenable for non-enterprise users.
Measure by measure
Usability
68Strong instant value with no-account free scans and platform-specific checks for AI builders; navigation is functional but crowded for a focused scanner tool.
Design
58Average visual execution with consistent cyan accents and a functional dark security-tool aesthetic, but dense competing text blocks and awkward 'vibe coders' headline tone reduce clarity.
Speed
82Excellent measured performance (92 mobile / 100 desktop Lighthouse) and marketed sub-15-second scans backed by live agent demo.
Security
72Strong header posture (11/12) and core detection focus; compliance mapping claimed but unverified by public audits or certifications.
Accessibility
80High automated score (96/100) with only minor contrast issue; responsive design and clear CTAs support usability, though explicit a11y docs absent.
Growth
28Extremely early-stage product (domain June 2026) with zero external traction, reviews, or community signals despite live free tier and content updates.
Improvement areas
- Lack of published security audits or compliance certifications despite marketing claims.
- Zero independent reviews or community presence for a live product.
- Dense hero copy and competing text elements on landing page reduce immediate clarity.
Design & Usability
Decloak.dev delivers a clean, dark-themed landing page with consistent cyan CTAs and an embedded live demo report that instantly shows value. The design sits in the average band due to dense sub-headlines and a headline tone that jars between 'vibe coders' casual and serious compliance features. Usability shines through the zero-friction free tier—no account, no card, results in under 15 seconds with platform fingerprinting for Supabase, Lovable, and Base44. Navigation covers multiple personas but feels slightly crowded. Overall, the product prioritizes immediate scanning over polished marketing polish, which aligns with its target of solo builders and small teams needing quick audits.
Speed & Security
Measured Lighthouse scores place speed firmly in the good-to-excellent range (92 mobile, 100 desktop) with sub-15-second scan claims backed by an agent investigation log demo. Security headers score 11/12 on probe, covering CSP, HSTS, and DMARC, while the tool's core strength is detecting real issues like exposed Stripe keys, publicly readable Supabase databases, and outdated jQuery CVEs. Marketing promises SOC2/ISO mapping and Enterprise DAST, but these lack independent verification. For a product this new, the passive scanning and header posture provide solid table-stakes security without enterprise overhead.
Accessibility & Growth
Accessibility earns strong marks from the 96/100 Lighthouse score, with only a single contrast-ratio failure noted; the responsive dark theme and high-contrast CTAs support broad usability. Growth is the clear weak point: registered June 2026 with no GitHub presence, zero third-party reviews, and no community signals despite active July 2026 journal posts. The product is in true early-stage mode—live free tier and pricing tiers exist, but traction metrics reflect its 0.1-year age. Peers like Qualys and Tenable have decades of reviews; Decloak is judged on trajectory, not absolute counts.
Conclusion
For vibe coders and indie builders shipping fast with AI tools, Decloak offers an accessible on-ramp to security awareness that enterprise scanners simply don't match on price or speed. As it matures, adding verified audits and community channels would accelerate adoption.
Suggestions for improvement
- Add explicit WCAG statement and fix the single contrast failure to push accessibility higher.
- Publish a security page or SOC 2 readiness note to substantiate compliance mapping claims.
- Create a public changelog or GitHub presence to build early developer trust and track momentum.
- Simplify hero copy to reduce text density and clarify the dual casual/compliance positioning.
Alternatives comparison
Named competitors, point by point. Nobody paid to appear here or to be left out.
 Decloak.dev |  Tenable |  Qualys | AppCheck | |
|---|---|---|---|---|
| Free tier availability | Yes - full 8-layer single-page scan, no account/card | No - enterprise only, paid DAST | Limited trial; core platform paid | Limited trial; full platform paid |
| Platform-specific AI builder checks (Supabase RLS, service_role keys) | Yes - fingerprinting for Lovable, Supabase, Base44, Bubble | No - general web/app scanning | No - broad vuln mgmt, no AI-builder focus | No - enterprise vuln mgmt, no platform-specific |
| Scheduled recurring scans + PDF evidence | Yes on Starter+; timestamped PDFs with attestation | Yes - enterprise scheduling and reporting | Yes - full scheduling and compliance reporting | Yes - advanced scheduling and exports |
| SOC2 / ISO 27001 control mapping | Yes - automated tagging to Annex A and Trust Services Criteria | Yes - enterprise compliance features | Yes - mature compliance modules | Yes - extensive compliance reporting |
| Enterprise DAST / active testing | Yes on Enterprise - forced browsing, CORS, authenticated scans | Yes - core DAST offering | Yes - full DAST and WAS | Yes - advanced active scanning |
Tenable
Industry-standard vulnerability management, but costs thousands per year. Decloak provides a free tier and lower-priced plans.
Qualys
Comprehensive security and compliance platform, but overkill for small teams. Decloak offers a simpler, cheaper alternative.
AppCheck
Enterprise vulnerability scanner with DAST, but expensive and requires interpretation. Decloak is faster and more affordable.
Comparing options? See Decloak.dev alternatives, scored side by side
Sources
What the review was written against. A verdict with no sources is an opinion.
More Productivity apps
View all Productivity
Qamarero
92An all-in-one hospitality software for restaurants and ba...

The Stack Newsletter
92A weekly newsletter delivering curated tech jobs, intervi...

EmbedMyReviews
92White-label reputation management software for agencies s...

StoryPad
92Privacy-first open source journal app with a continuous t...

Puzzly – B2B Lead Generation & Sales Intelligence Platform
92Puzzly is an all-in-one B2B lead generation platform that...

Notion
92All-in-one AI workspace for docs, projects, and knowledge...

Vibe Coding Agent Skills
92A free, open-source platform offering 110 AI agent skills...

CC Switch
91Open-source desktop app for switching AI coding providers...

username.md
90One verified handle for your online identity, readable by...

What the GIF
89Frame-perfect video-to-GIF maker that runs entirely in yo...

AuditCloser
89White-label website audits that close deals for digital a...

NudgeWin
89Automated quote follow-up for trades and service businesses.
A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.
