A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.
A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.
A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.
Cycling through all six. Tap any point to stop.
Measured on six things
A zero-config AI-powered vulnerability scanner automating...
Excellent for security teams avoiding credential sharing. Supports partial/targeted scans, subdomain scanning, branded reports, and enterprise on-prem options. Strong for DevOps in CI/CD pipelines.
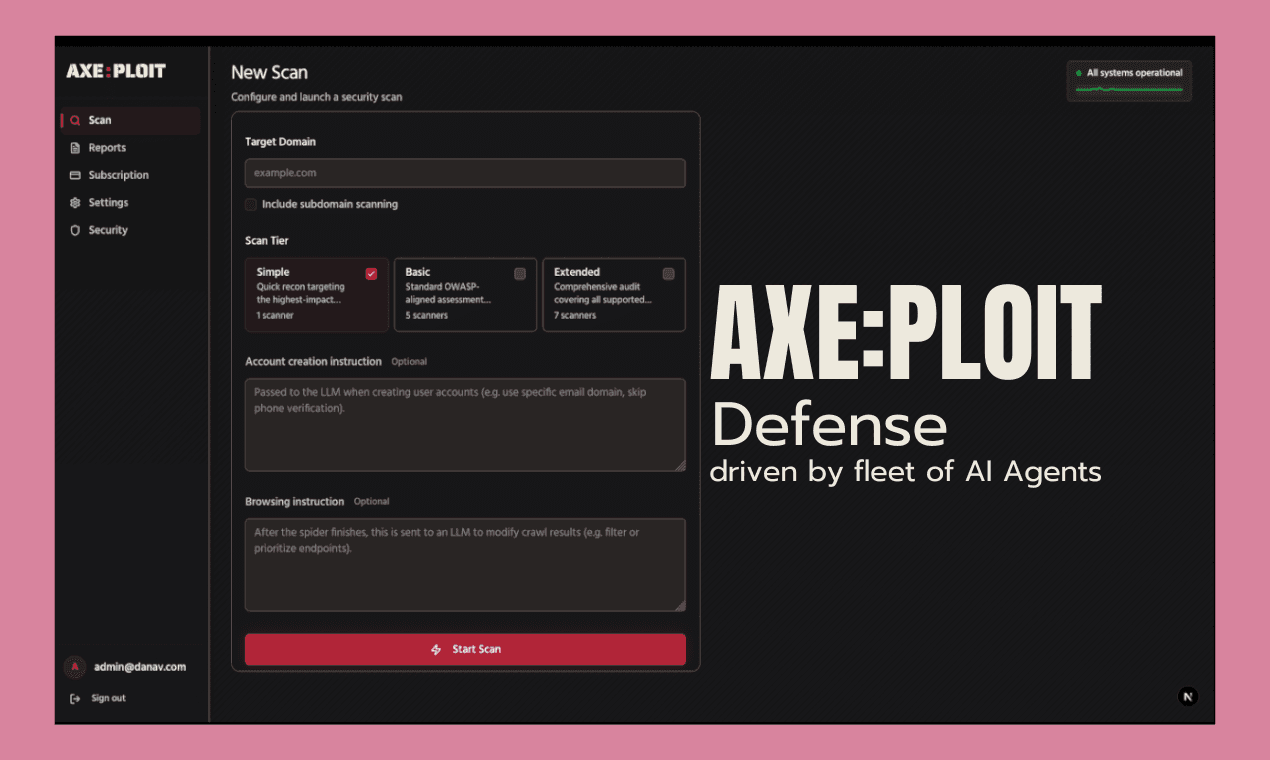
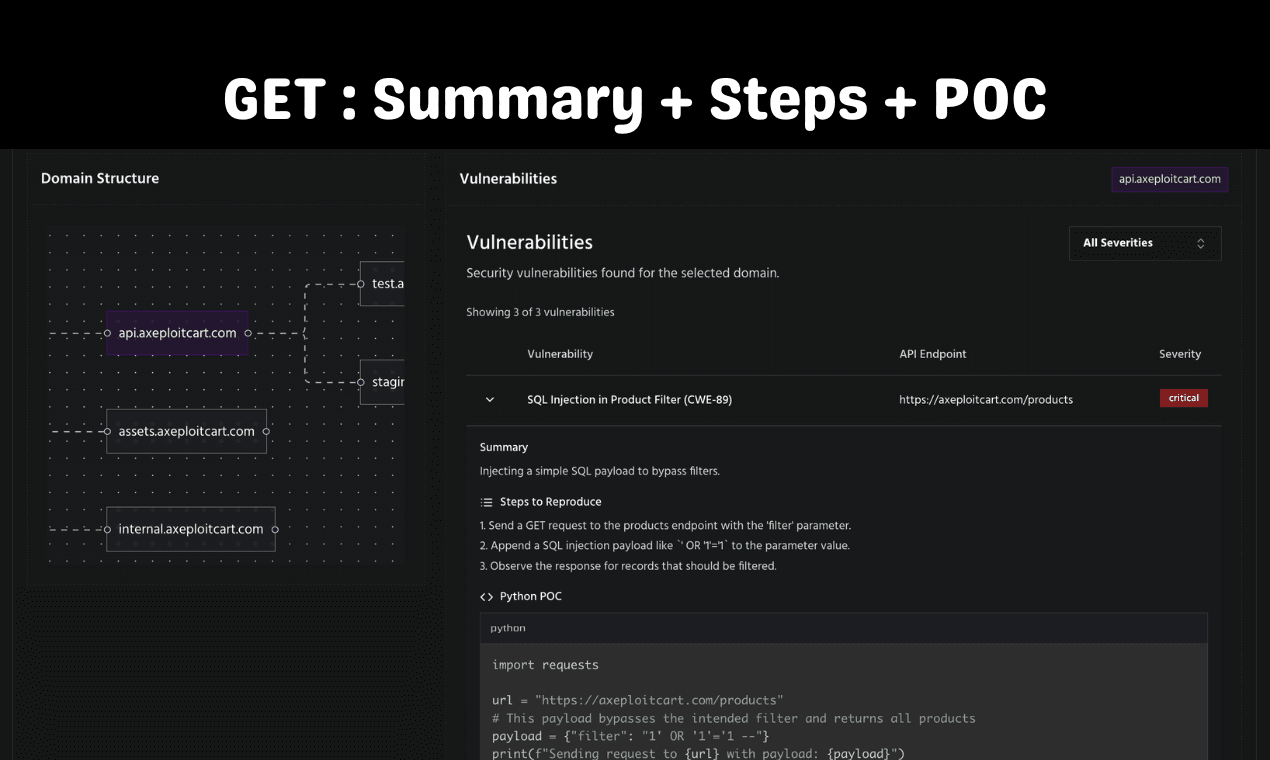
Axeploit is a game-changing AI-powered vulnerability scanner that redefines offensive security by automating complex penetration testing tasks with zero manual configuration. As a tech-savvy reviewer, I've been impressed by how it tackles the tedious aspects of security scanning—like setting up credentials and recording user flows—by leveraging a fleet of AI agents that act like real users. It autonomously signs up for applications, verifies accounts via OTP, and navigates platforms to uncover over 7,500 vulnerabilities, from common SQL injections to advanced business logic flaws. What sets Axeploit apart is its continuous learning; it gets smarter with every scan, adapts to frontend changes in real-time, and integrates seamlessly into CI/CD pipelines with Slack alerts and custom report exports. For teams tired of false positives and hidden costs in traditional tools, Axeploit offers a scalable solution with pricing plans from $199/month, making it a must-try for modern cybersecurit...
Drawn from the product itself, not from a survey.
Demographic
Security teams in mid-sized tech companies or startups
Pain points
Manual setup for vulnerability scans, high false positives, and time-consuming integration with legacy tools
Primary needs
Automated, accurate scanning with zero configuration to streamline security workflows
Demographic
Penetration testers and ethical hackers
Pain points
Inability to test authentication flaws like OTP and email verification without sharing credentials
Primary needs
AI-driven tools that simulate real user behavior to detect advanced vulnerabilities
Demographic
DevOps and engineering teams in enterprises
Pain points
Hidden costs from manual API integrations and lack of real-time alerts in CI/CD pipelines
Primary needs
Seamless integration, scalable scanning, and custom reports for continuous monitoring
Written by AI from measured evidence, scored out of 100.
Axeploit delivers on its promise of AI-driven, zero-config offensive security that simulates real users for comprehensive testing traditional tools struggle with. Strengths in autonomous auth testing, false-positive reduction, CI/CD integration, and continuous learning make it compelling for security teams frustrated with manual setups and high costs. The product is still maturing (gated onboarding, batch access to monitor performance), but early demos and 'No Exploit, No Report' philosophy are promising. At $199/mo starter, it targets mid-market teams effectively. It won't fully replace expert pentesters but can significantly augment them by handling repetitive scanning and auth flows. Overall a strong innovator in the crowded pentest tool space.
True zero-config experience stands out. AI agents handle signup, OTP verification, and real-user flows autonomously. Smart targeting and CI/CD integration make it accessible for non-expert security teams.
Clean, modern SaaS site with demo flows and clear value props. Dark-themed security aesthetic, intuitive navigation, and engaging animated scan examples.
Autonomous agents complete full auth-to-exploit cycles quickly in demos (discovered 125 APIs, 20+ vulns). Real-time Slack alerts and adaptive layout intelligence reduce manual wait times dramatically.
'No Exploit, No Report' philosophy with verified PoCs slashes false positives. Uses real contact details for auth testing, covers 7,500+ vulns including business logic, IDOR, auth bypass, and zero-days via updated CVE database.
Excellent for security teams avoiding credential sharing. Supports partial/targeted scans, subdomain scanning, branded reports, and enterprise on-prem options. Strong for DevOps in CI/CD pipelines.
Continuous learning from every scan, real-time frontend adaptation, seamless Slack/webhook/CI/CD integration, custom exports, and scalable enterprise plans. Positions well for growing security programs moving beyond manual testing.
Axeploit's website and product promise a refreshing break from clunky legacy scanners. The design is professional and focused on demonstrating autonomous AI agents that sign up, verify via OTP using real contact details, navigate, and test like actual users. Usability is the standout — zero manual configuration for credentials or user flows is a genuine differentiator from Burp Suite or OWASP ZAP, which often require significant setup and expertise. Security teams in startups or mid-sized companies tired of false positives and credential sharing will appreciate the 'No Exploit, No Report' approach that only surfaces verified PoCs. The demo flow (finding signup, handling mobile OTP, discovering 125 APIs and 20+ vulns) is impressive on paper. However, current gated access for onboarding (to ensure guardrails) tempers the 'zero config' claim for immediate use.
Speed shines in automated auth-to-exploit cycles and real-time alerts, reducing the weeks of manual pentesting into faster cycles with Slack notifications and API/webhook triggers for CI/CD. Security depth is strong with coverage of 7,500+ vulnerabilities — from SQLi and IDOR to advanced business logic and auth flaws (which cause >30% of issues but are poorly tested traditionally). Continuous CVE updates and layout-aware intelligence help it adapt without breaking. Compared to Nessus (more network-focused traditional scanning) or Burp Suite (powerful but manual-heavy), Axeploit's AI fleet removes tedious setup. False positive reduction via verified exploits is a major claimed advantage. Enterprise features like private deployment and unlimited scans address scalability and compliance needs that open-source ZAP can't match easily.
Highly accessible for modern DevOps and engineering teams: no need to share creds, supports targeted scans on new features or high-risk endpoints, subdomain scanning, and seamless integration without ongoing manual API maintenance. This directly solves pain points of legacy tools with hidden integration costs (~$2k/year maintenance cited). Growth potential is high as the system learns per scan and scales via enterprise plans (unlimited runs, on-prem, dedicated support). For penetration testers, it automates the boring parts so they can focus on novel logic flaws. Pricing starts reasonably at $199/month (yearly discount 25%), with custom enterprise. Compared to free ZAP or expensive Nessus/Burp Pro, it offers a middle-ground automated AI solution that could grow with teams moving security left in CI/CD. Long-term success depends on real-world accuracy and avoiding over-promising on zero-days.
Conclusion
If you're drowning in false positives, credential management headaches, or slow integration with legacy scanners, Axeploit is worth requesting access for. Its AI agents represent the future of scalable offensive security. Just temper expectations with the current early-stage access model. Modern security programs should test it alongside Burp or ZAP to see the automation gains firsthand.
Named competitors, point by point. Nobody paid to appear here or to be left out.
 Axeploit |  Burp Suite |  OWASP ZAP |  Nessus | |
|---|---|---|---|---|
| Automation Level | Fully autonomous AI agents (signup, OTP, real-user flows); zero manual config | Automated scanner + strong manual tools; requires significant setup and expertise | Automated scanning with proxy; open-source but needs configuration and scripting | Primarily automated traditional scanning; less focus on complex web auth/business logic |
| False Positive Handling | 'No Exploit, No Report' with verified PoCs; claims major reduction | Good with manual verification; automated results can have noise | Automated alerts often require manual triage; known for some false positives | Strong plugin-based detection with severity ratings; can still produce noise in web apps |
| Auth & Business Logic Testing | Excellent — native OTP/email verification, IDOR with multiple accounts, advanced logic flaws | Very strong with manual testing and extensions; requires human expertise for logic flaws | Basic automated auth testing; limited on complex business logic without custom scripts | Limited for deep web app auth/business logic; stronger on network/config vulns |
| CI/CD & Alert Integration | Native webhooks, API, Slack real-time alerts, seamless pipeline integration | Good via extensions and CLI; requires more custom setup | Strong open-source automation for CI/CD; popular in DevSecOps | Enterprise integrations available but more traditional reporting focused |
| Pricing / Accessibility | Starts at $199/mo (yearly discount); Enterprise custom with on-prem. Gated onboarding | Professional ~$449/year; Community free but limited. Widely accessible | Completely free and open source; no barriers | Professional ~$4,500+/year; Enterprise licensing. Higher cost |
Burp Suite
A widely used web vulnerability scanner with manual and automated testing features, but requires more setup and expertise.
OWASP ZAP
An open-source security tool for finding vulnerabilities in web applications, though it lacks the AI automation of Axeploit.
Nessus
A comprehensive vulnerability assessment tool for networks and applications, but focused more on traditional scanning methods.
Comparing options? See Axeploit alternatives, scored side by side
What the review was written against. A verdict with no sources is an opinion.

Sidenty is a professional digital identity protection ser...

A native macOS process explorer and advanced monitor that...

Real-device browser automation for AI agents

Native macOS SSH, SFTP & RDP client with a Keychain-backe...

Password manager with no email, no account, no tracking. ...

Reveal No Caller ID, unknown numbers, and private callers...

CyberSafe Pro is a completely offline password manager that stores your credentials securely on your device using military-grade encryption.

A security solution that integrates VPN access with identity platforms to reduce network vulnerabilities and protect against zero-day exploits.

AuditReady è una piattaforma per gestire conformità, controlli, responsabilità ed evidenze in un unico ambiente, con supporto per GDPR, NIS2, DORA, ISO 27001, AI Act e Modello 231.

Advanced parental control software for Windows & Android

An encrypted digital legacy service that securely deliver...

A specialized tool that monitors security.txt file expiration dates to prevent missed vulnerability disclosures with simple email or calendar reminders.
A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.
