Cycling through all six. Tap any point to stop.
Measured on six things
See which cookies and requests fire before Accept
Growth
60A real, specific problem — proving Reject All actually blocks pixels — with scenario-based evidence as a genuine wedge. Early-stage (domain registered 2026-05-30), so traction is context, not the score.
Screenshots
1 / 1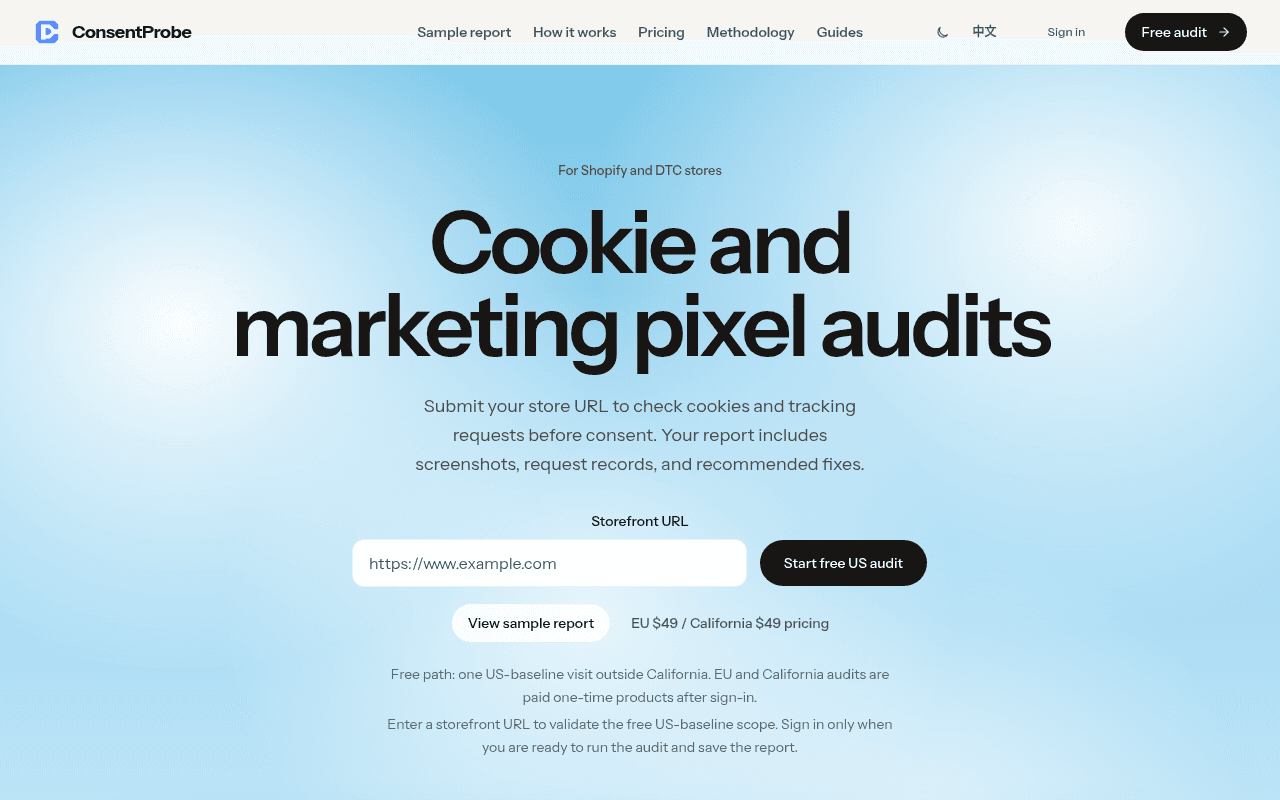
About this app
A cookie banner on the page doesn't show what the browser sends after a shopper clicks Reject All, and ConsentProbe records that. Paste a Shopify or DTC store URL. An isolated browser visits the store, records each cookie, storage write and network request, and saves screenshots of the banner. Every finding points to the request or screenshot it came from, so a developer can check it. The free audit is one US-baseline visit, before anyone answers the banner. The EU audit ($49, one-time) visits the same URL fresh, after Reject All and after Accept All, and lists hosts that still received requests after Reject. The California audit ($49, one-time) compares a baseline visit with one that sends Global Privacy Control. ConsentProbe is not a Shopify app and installs nothing on the store. Reports are technical records, not legal advice.
Key features
- 1Isolated-browser storefront audits recording cookies, storage writes, network requests, and banner screenshots.
- 2Scenario-based captures: free US baseline, EU fresh/reject/accept ($49), California GPC pair ($49), Global 2 ($79).
- 3Evidence-linked findings — every result points to the request, cookie, or screenshot it came from.
Target customer profile
Drawn from the product itself, not from a survey.
Scout Review
Written by AI from measured evidence, scored out of 100.
ConsentProbe is a focused, well-built niche tool that answers a question most cookie banners quietly dodge: what actually fires after a shopper clicks Reject All. The site is fast and accessible, the free US-baseline audit is a smart on-ramp, and the evidence-linked report format is the real product. Weaknesses are real but not fatal: a template-grade hero, a $49 paywall on the scenarios that matter most, and security headers that a privacy-auditing tool should arguably have nailed. It's early, it's narrow, and it knows exactly what it's for — which is more than most SaaS can say.
Measure by measure
Usability
68URL input plus 'Start free US audit' is instantly actionable, and a $0 baseline audit lets you see the report format before paying. Sample report, methodology, and checklist guides give solid self-serve support.
Design
70Clean, readable hero with strong headline contrast and a clearly prioritized CTA. Spacing is disciplined, but the light-blue gradient and centered layout read as template-generic, and the sub-form text is cramped and low-contrast.
Speed
74Lighthouse mobile 89/100 and desktop 98/100, with CLS 0 and FCP 1.5s. LCP of 3.3s on mobile is the one soft spot, but overall the site is light and snappy.
Security
62HTTPS enforced with HSTS, X-Content-Type-Options, Referrer-Policy, and SPF — 7/12 header checklist points. Missing CSP, frame protection, Permissions-Policy, and DMARC, and no published audit or compliance certification.
Accessibility
80Lighthouse accessibility 96/100 with only a color-contrast failure flagged. A language switcher signals multi-language support, though no WCAG conformance statement is published.
Growth
60A real, specific problem — proving Reject All actually blocks pixels — with scenario-based evidence as a genuine wedge. Early-stage (domain registered 2026-05-30), so traction is context, not the score.
Improvement areas
- Security headers incomplete: no CSP, frame protection, Permissions-Policy, or DMARC; no published compliance certification.
- Key regional scenarios sit behind a $49 paywall, so the free path shows format more than substance.
- No WCAG conformance statement, and a flagged color-contrast issue on the sub-form text.
Design & Usability
ConsentProbe's homepage is competent and clean: a bold headline, a URL field paired with a 'Start free US audit' button, and a sample report one click away. The visual audit rated it 'good' — strong contrast, disciplined spacing — but the light-blue gradient hero is the same template every SaaS ships, and the small text under the form is cramped and low-contrast. Usability is the stronger half: the free $0 US-baseline audit lets you see the report format before committing, and the site backs it with methodology, guides, and storefront checklists. The friction is that the genuinely useful regional scenarios (EU, California) sit behind a $49 paywall, so the free path shows format more than substance.
Speed & Security
Speed is a clear strength: Lighthouse mobile 89/100 and desktop 98/100, with zero layout shift and a 1.5s first contentful paint. The only blemish is a 3.3s mobile LCP. Security is mid-tier: HTTPS is enforced with HSTS, and X-Content-Type-Options, Referrer-Policy, and SPF are all present, but the probe found no CSP, no frame protection, no Permissions-Policy, and no DMARC — 7 of 12 checklist points. There's no published SOC 2, ISO, or pen-test evidence either. For a tool whose whole pitch is auditing other sites' data handling, the missing hardening headers are a noticeable gap, though the product's scoped, no-install model keeps its own attack surface modest.
Accessibility & Growth
Accessibility scores well: Lighthouse 96/100 with a single color-contrast failure, and a language switcher signals multi-language intent, though no WCAG statement is published. Growth is a judgment on the idea, and the idea is genuinely good — 'does Reject All actually stop the TikTok pixel?' is a real, checkable question that store owners and developers care about, and scenario-based browser capture with evidence-linked findings is a concrete differentiator versus generic CMP dashboards. The honest limit: it's a point-in-time audit, not a recurring subscription, and it depends on stores caring enough to pay $49 to be told they're leaking. The domain is only months old, so traction is unproven — but the wedge itself is sound.
Conclusion
If you run a Shopify or DTC store and you've ever wondered whether your CMP is actually doing anything, the free audit is a low-cost way to find out. Go in expecting a technical record, not a legal verdict, and budget for the $49 EU or California run if compliance is the real question. The product is young and its security posture could be tighter, but the core idea — receipts for your cookie banner — is worth the click.
Suggestions for improvement
- Publish a WCAG conformance statement and fix the flagged color-contrast issue on the sub-form text.
- Add CSP, frame protection, Permissions-Policy, and DMARC to match the privacy-auditing positioning.
- Offer a discounted or sample EU/California scenario so the free path shows real regional value, not just format.
- Consider a lightweight recurring monitoring tier — point-in-time audits leave repeat revenue on the table.
Alternatives comparison
Named competitors, point by point. Nobody paid to appear here or to be left out.
 ConsentProbe | ||
|---|---|---|
| Price for a regional (EU/California) audit | $49 one-time per region; Global 2 bundle $79 | Not provided |
| Free entry point | Free US-baseline audit ($0) | Not provided |
| Evidence format | Request/cookie logs, screenshots, evidence IDs | Not provided |
| Installation required | None — not a Shopify app, installs nothing | Not provided |
Comparing options? See ConsentProbe alternatives, scored side by side
More Analytics apps
View all Analytics
LTX 2.3 AI Video Generator
91Fast, open-source AI video generator with 4K support, mul...

CitableReport
89CitableReport is an AI visibility audit:

ButterKit
82macOS app for App Store screenshots: 3D mockups, auto-tra...

PERM Processing Time: Current DOL Queue & History
88PERM Processing Time is an independent data analysis platform that helps users navigate the U.S. Department of Labor’s permanent labor certification process.

Askray
88See who ChatGPT, Gemini & Claude recommend instead of you...

SiftingIO - Market Data API
88Real-time & historical market data API for stocks, forex,...

Sonar
87Free website tracking checker. Paste a URL and Sonar crawls your site from the outside, then reports what's running and the problems it can prove.

Reptor
85Reputation monitoring across Google, AI search engines, reviews, news and social media, with sentiment analysis per mention.

Xquik
85Search X tweets, export followers & monitor accounts through REST, MCP & SDKs.

Timix - A Modern Timer
84Turn timers into powerful routines with automation, widge...

Activity Racoon
82Engineering intelligence platform automating sprint analy...

LLM Reference
82Decision-support platform for engineers choosing the righ...
A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.