Cycling through all six. Tap any point to stop.
Measured on six things
Autonomous AI pentesting suite with 7-agent red team, 275...
Accessibility
58Lighthouse a11y 83/100 with real failures: unnamed buttons, insufficient contrast, non-sequential headings, color-only links, small touch targets. No WCAG statement or a11y page found. Mid-band — the failures are concrete but not catastrophic.
Screenshots
1 / 4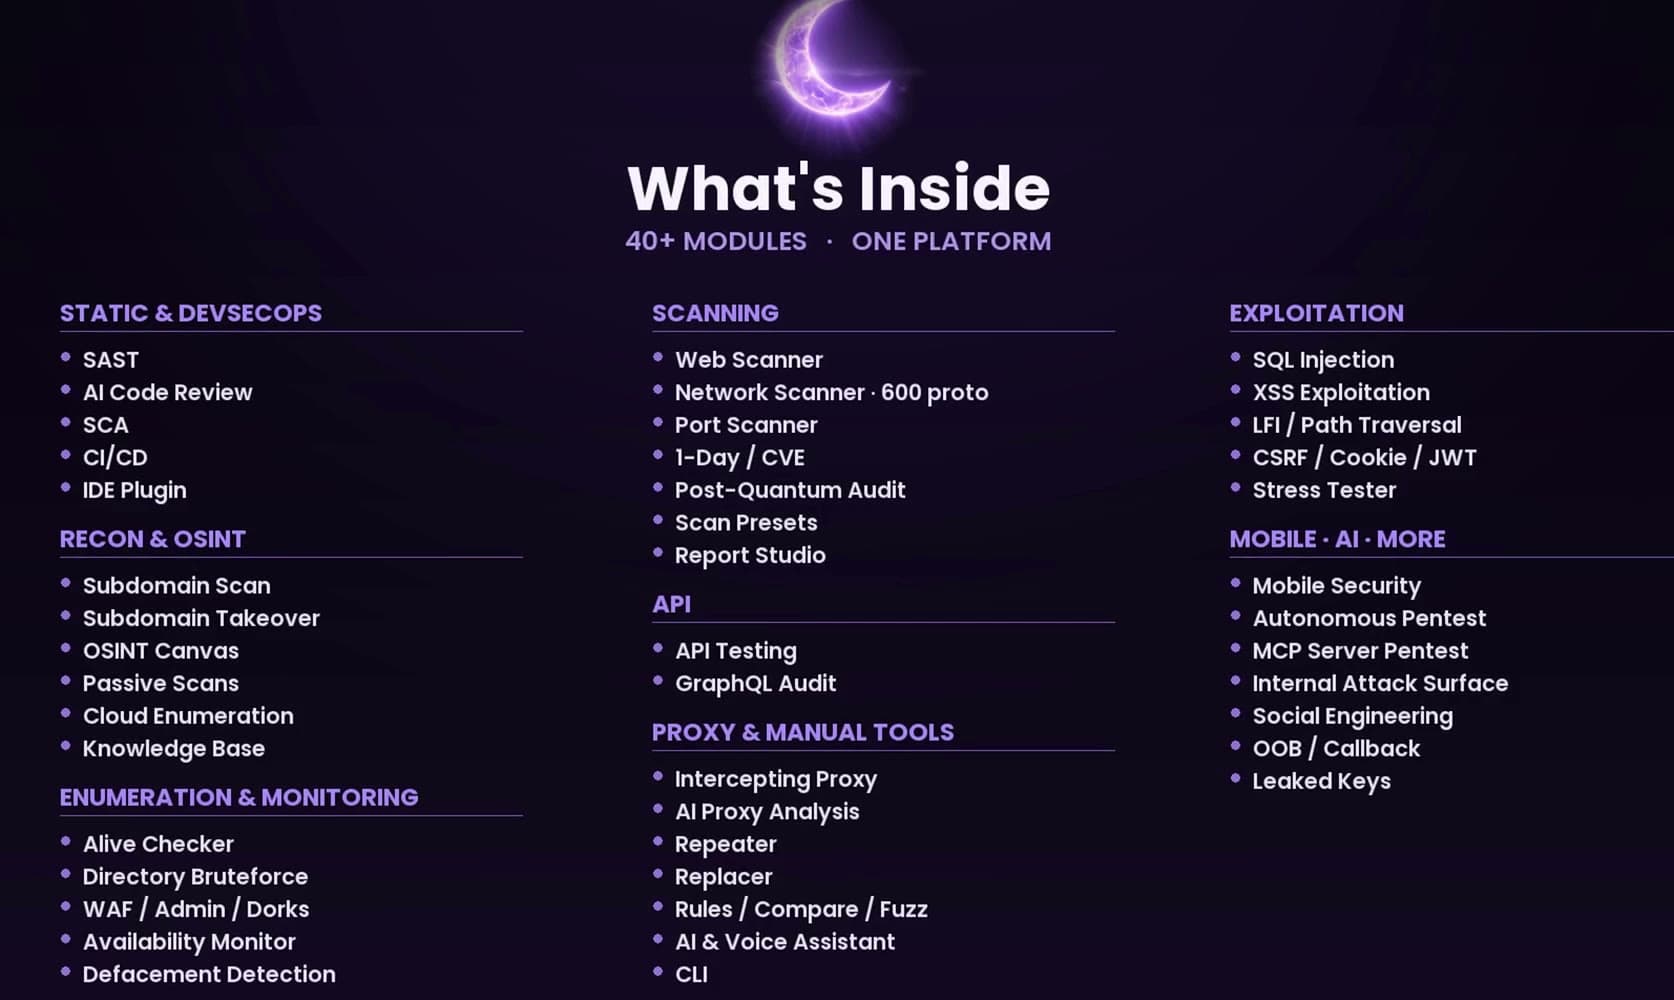
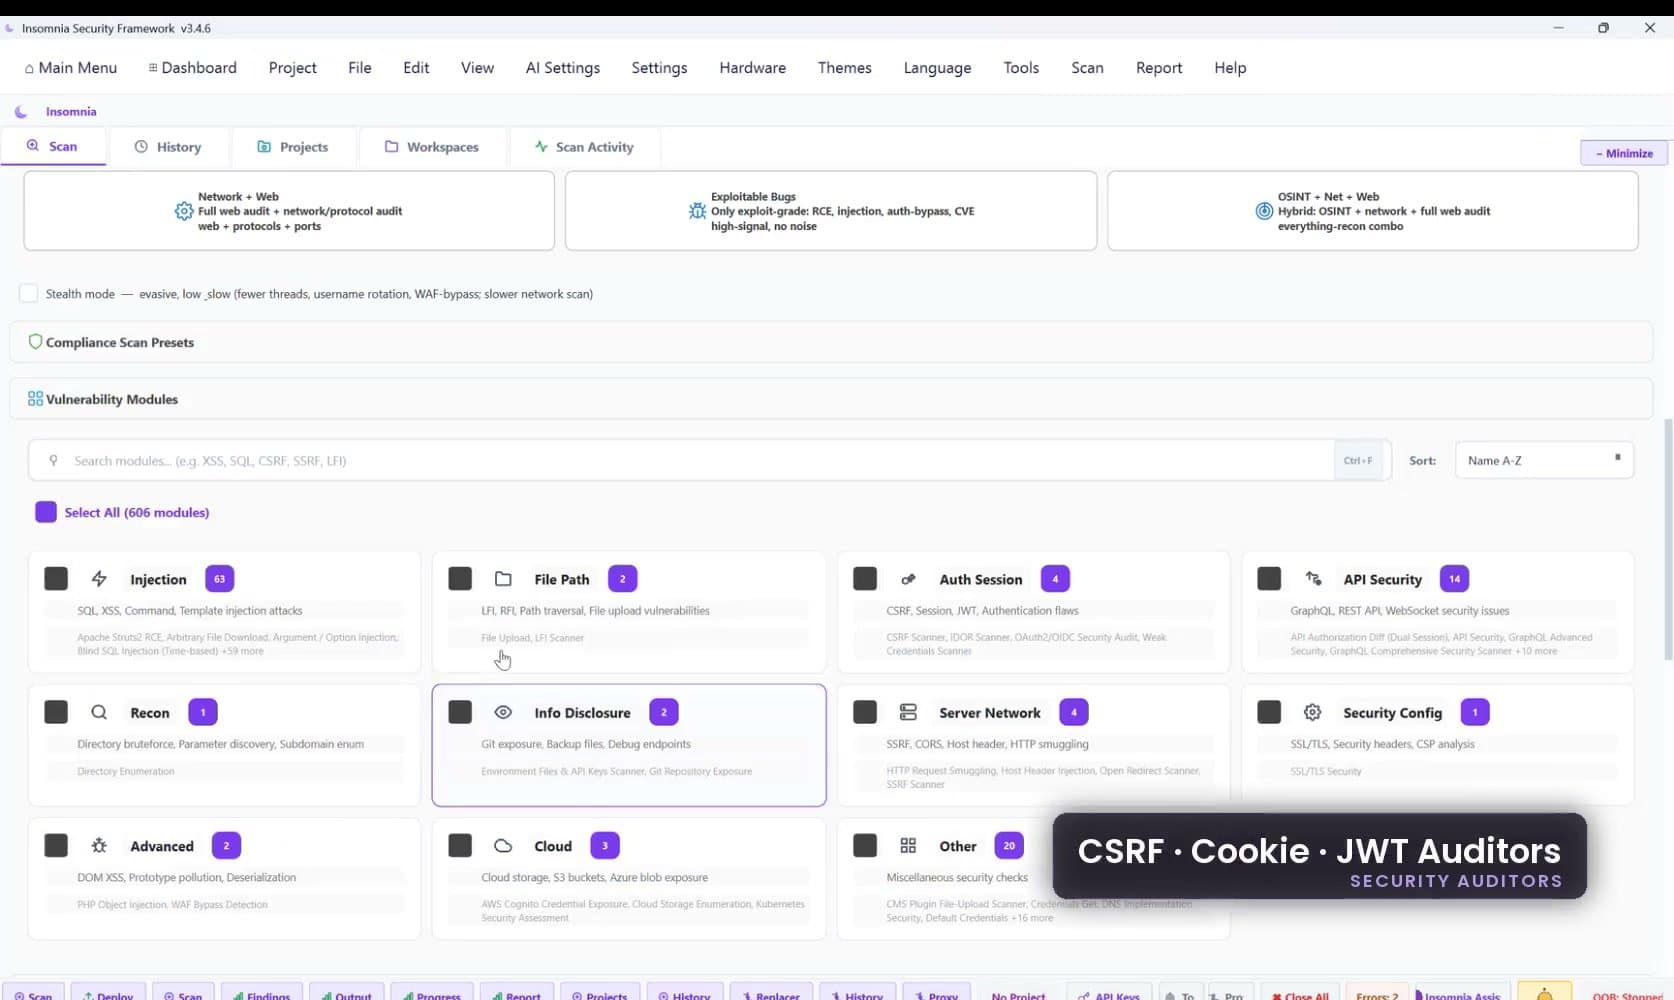
About this app
Insomnia is a comprehensive, AI-driven offensive security platform. It stands out with its autonomous 7-agent AI red team that collaborates to find, validate and exploit vulnerabilities. Covering web, API, network, Active Directory, OSINT, mobile and source code, it packs 275+ modules into a single suite. Key features include a free SAST engine (16 languages, SARIF) with VS Code and JetBrains plugins, CI/CD integration, a 30K+ CVE database, exploitation tools and professional PDF, DOCX or HTML reports with CVSS scoring. With strong benchmark results against Semgrep and SonarQube, it is a powerful alternative to disconnected scanning tools. Ideal for security teams, pentesters and developers shifting left. Runs on Linux, macOS and Windows. Freemium: free Community Edition, Advanced from $149/mo.
Key features
- 1Autonomous 7-agent AI red team that collaborates to find, validate and exploit vulnerabilities across web, API, network, AD, OSINT, mobile and source code
- 2Free SAST engine (16+ languages, SARIF output) with VS Code and JetBrains plugins plus a CI/CD wizard for shift-left pipelines
- 3275+ modules, 30K+ CVE database, exploitation tools, and professional PDF/DOCX/HTML reports with CVSS scoring
Target customer profile
Drawn from the product itself, not from a survey.
Demographic
Penetration Testers & Red Teams
Pain points
Juggling multiple tools, manually stitching reports, time-consuming validation of findings
Primary needs
Unified platform with automated exploitation and professional reporting
Demographic
Security Managers & MSSPs
Pain points
High licensing costs per tool, inconsistent skill levels across team, alert fatigue
Primary needs
Cost-effective all-in-one solution with AI assistance for junior staff
Demographic
Developers & DevSecOps
Pain points
Late vulnerability detection, noisy SAST tools, complex CI/CD integration
Primary needs
Shift-left security with low false positives, easy pipeline integration
Scout Review
Written by AI from measured evidence, scored out of 100.
Insomnia is an ambitious AI-driven offensive security suite that tries to be the one platform for pentesters, DevSecOps and students — and mostly delivers on the marketing side. The site is fast, on-brand, and backed by real product screenshots and 43 demo videos. The docs are genuinely usable with quick-start commands and interactive wizards. The free SAST CLI with IDE plugins is the sharpest wedge against Semgrep, and the AI red-team story differentiates against Cobalt and Intruder. The gaps are concrete: missing HSTS, no public compliance attestations, and a Lighthouse accessibility score of 83 with real failures. The pricing ladder is overbuilt for a product this young.
Measure by measure
Usability
63Docs ship a five-command quick start, interactive wizards for flag-averse users, and 43 categorized demo videos. Free Community Edition plus a no-install browser playground make first value cheap. Five pricing tiers (Community/Advanced/Pro/Enterprise/Military/Gov) is a lot to navigate.
Design
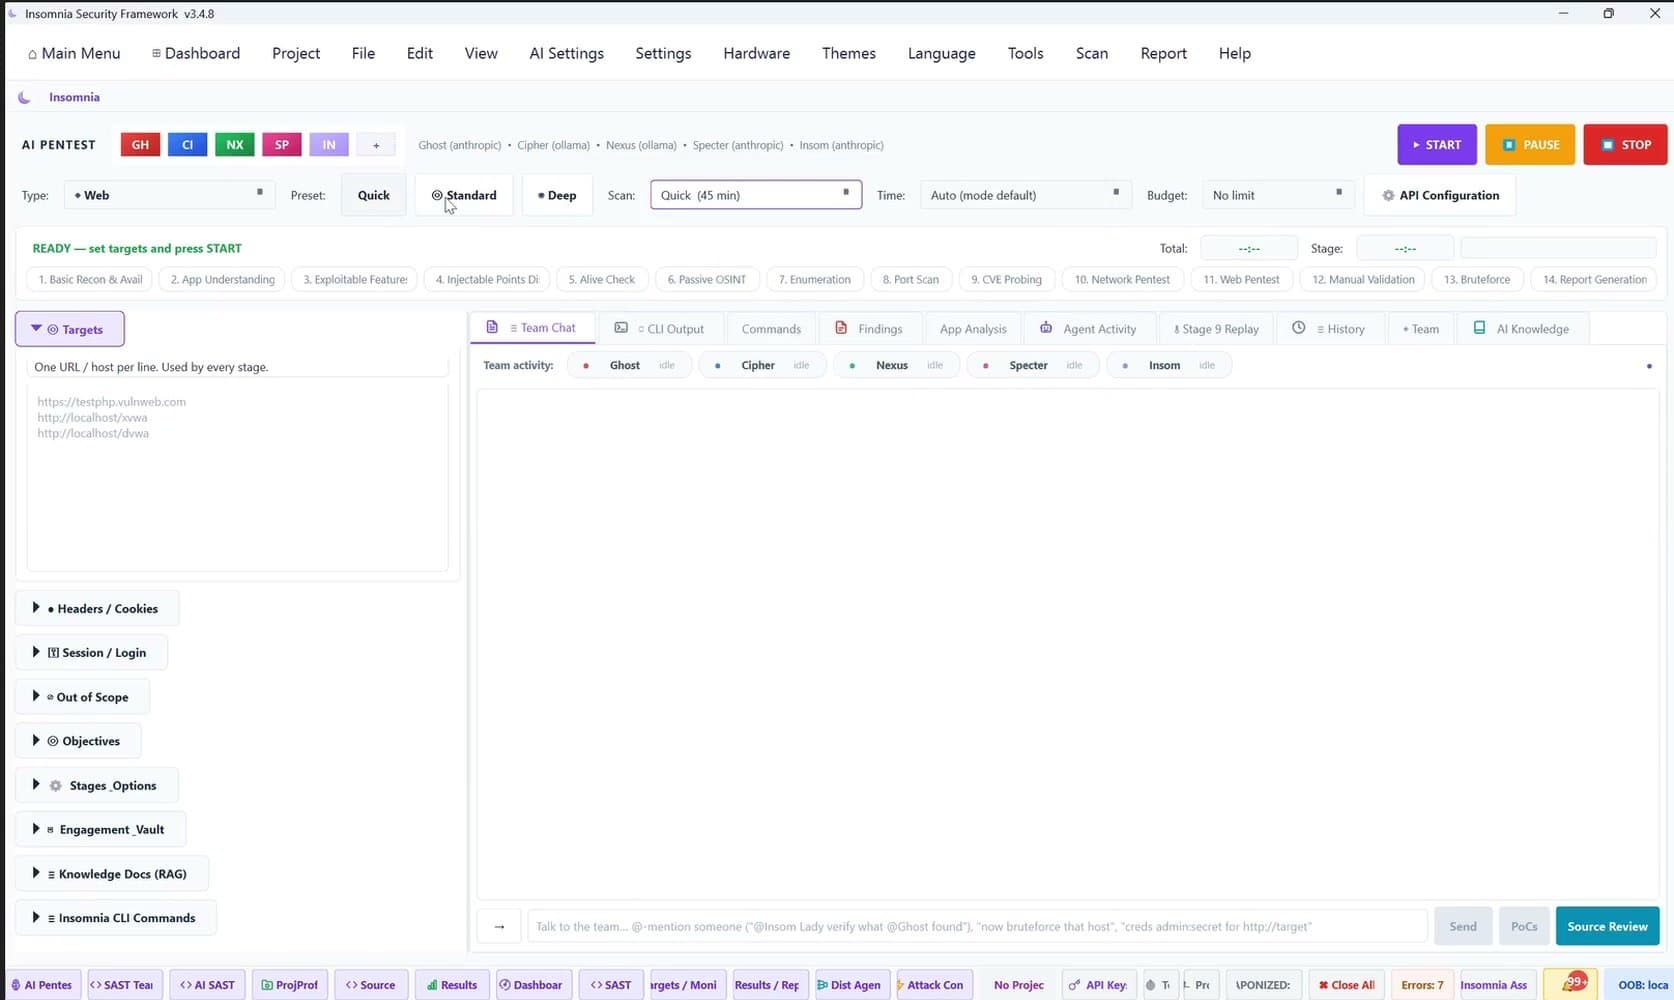
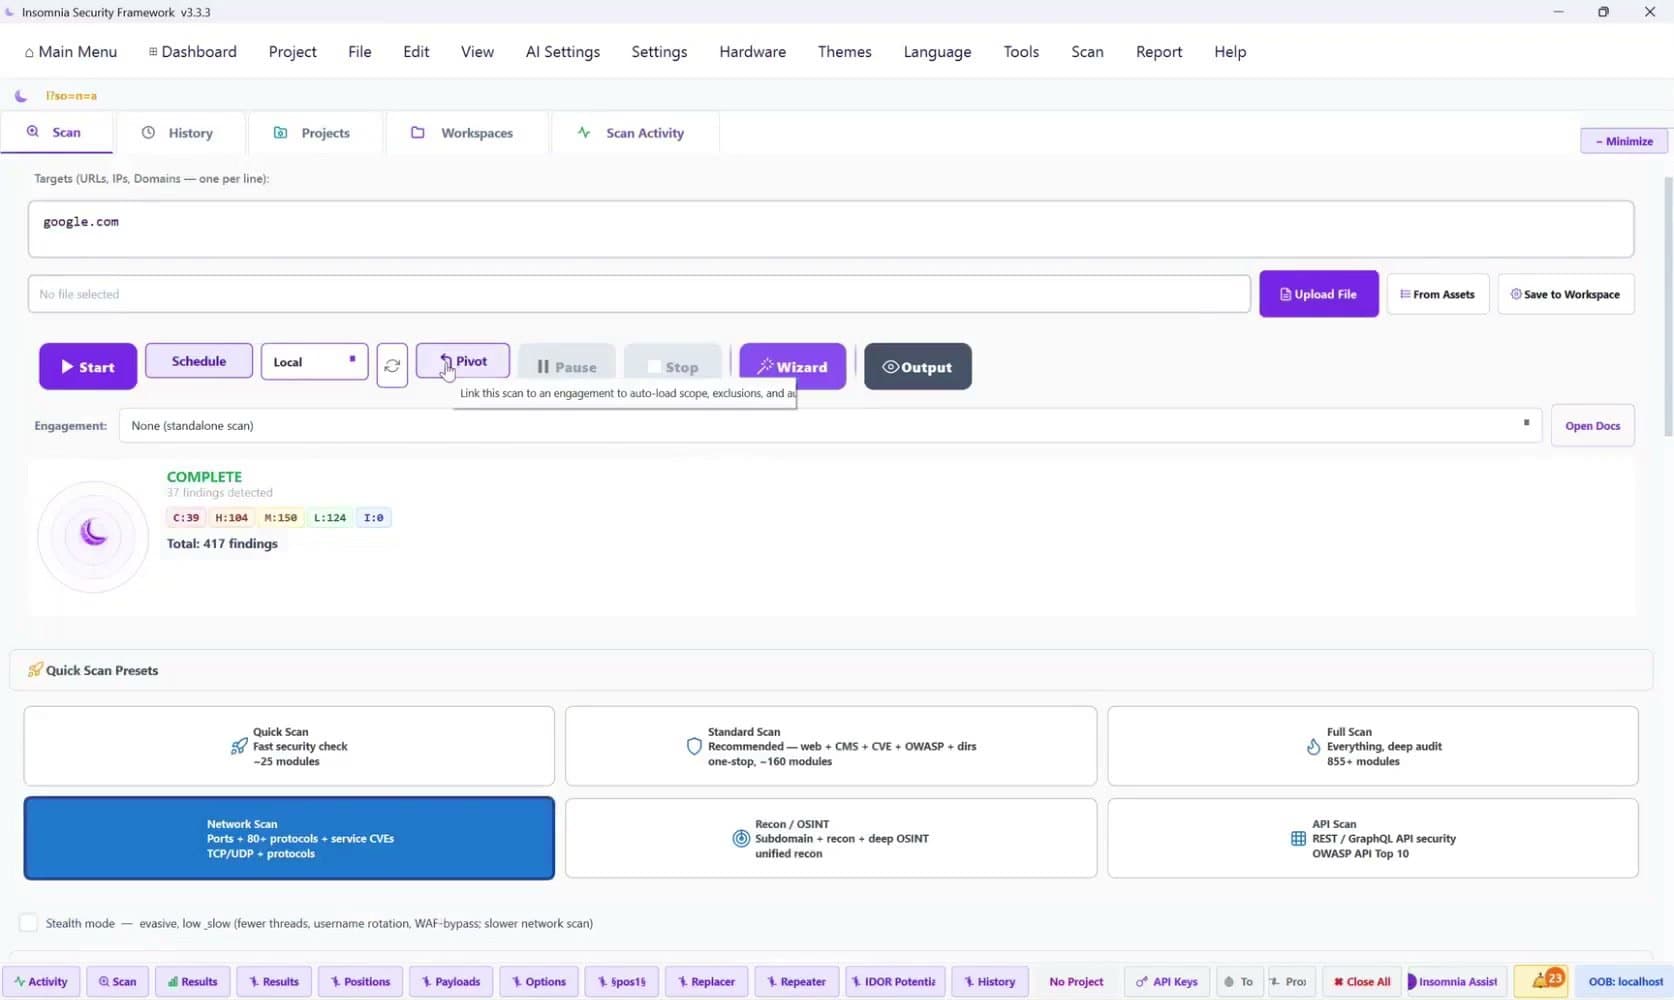
71Coherent dark-purple security aesthetic with real product screenshots (decision tree, pipeline canvas, AI chat) instead of stock art. Dense hero copy and a crowded six-link nav plus search and language picker hold it back from the top of the band.
Speed
88Lighthouse mobile 98/100 (LCP 2.0s, CLS 0, TBT 0ms) and desktop 100/100. The marketing site is genuinely fast — static-feeling, no layout shift, no main-thread jank. Among the best in the category on raw page performance.
Security
74HTTPS enforced with CSP, frame protection, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, SPF and DMARC (10/12 probe points). HSTS is missing and no SOC 2/ISO/bug-bounty page surfaced. Enterprise tiers advertise SSO/LDAP and air-gapped deployment.
Accessibility
58Lighthouse a11y 83/100 with real failures: unnamed buttons, insufficient contrast, non-sequential headings, color-only links, small touch targets. No WCAG statement or a11y page found. Mid-band — the failures are concrete but not catastrophic.
Growth
68Real problem (tool sprawl, noisy SAST, slow reporting) with a specific wedge: free SAST CLI + IDE plugins + CI/CD wizard aimed at shift-left developers, plus an AI red-team story for pentesters. Category has headroom; the six-tier pricing risks diluting focus.
Improvement areas
- Missing HSTS header and no public SOC 2 / ISO 27001 / bug-bounty page despite enterprise and government tier claims
- Lighthouse accessibility 83/100 with unnamed buttons, insufficient contrast, non-sequential headings and small touch targets
- Six pricing tiers (Community/Advanced/Pro/Enterprise/Military/Gov) overcomplicate the buying decision for a young product
Design & Usability
The homepage is a competent, on-brand dark-purple security site with real product screenshots — decision trees, pipeline canvases, AI chat panels — rather than the stock-photo-and-gradient template most competitors ship. Design loses points for a dense hero paragraph and a nav bar doing too many jobs at once. Usability is stronger: the docs page opens with five copy-paste commands, every command has an interactive wizard when you omit the target, and 43 categorized demo videos plus a no-install browser playground mean you can evaluate the product before installing anything. The five-tier pricing ladder (Community, Advanced, Pro, Enterprise, Military, Gov) is where navigation gets muddy — most buyers just want to know which tier unlocks the AI agent.
Speed & Security
Speed is the standout: Lighthouse mobile 98/100 with LCP 2.0s, CLS 0 and TBT 0ms, desktop a clean 100/100. The marketing site is genuinely fast and stable, which matters when your pitch is 'watch the AI red team work in real time.' Security is solid but not airtight: HTTPS is enforced with CSP, frame protection, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, SPF and DMARC all present — 10 of 12 probe points. The two gaps are HSTS (missing) and the absence of any public SOC 2, ISO 27001, or bug-bounty page in the collected content. For a vendor selling offensive security to enterprises and governments, those are the receipts buyers will ask for first.
Accessibility & Growth
Accessibility is the weakest dimension: Lighthouse 83/100 with concrete failures — buttons lacking accessible names, insufficient color contrast, non-sequential heading order, color-only link distinction, and undersized touch targets. No WCAG statement or accessibility page was found. Growth is the more interesting story: the problem (tool sprawl, noisy SAST, manual report stitching) is real and the wedge is specific — a free SAST CLI with VS Code and JetBrains plugins plus a CI/CD wizard aimed squarely at shift-left developers, alongside the AI red-team story for pentesters. Against Cobalt (human pentest), Intruder (automated scanning) and Semgrep (SAST only), the unified-platform pitch has room. The risk is that six pricing tiers and a Military/Government ambition dilute focus before the core wedge is proven.
Conclusion
If you're a pentester tired of stitching reports from five tools, or a DevSecOps lead who wants SAST in the pipeline without a SaaS contract, Insomnia is worth a real evaluation — the free Community Edition and browser playground make that cheap. If you're an enterprise buyer, ask for the SOC 2 report and the HSTS header before you sign anything. The product's ambition is real; the compliance paperwork needs to catch up.
Suggestions for improvement
- Set the HSTS header — it's one line and it's the first thing a security buyer checks.
- Publish a SOC 2 or ISO 27001 page (or a clear 'in progress' note) to back the Enterprise tier.
- Fix the six Lighthouse a11y failures: name the buttons, raise contrast, order headings, size touch targets.
- Collapse the six pricing tiers into three and put the AI agent on the comparison table where buyers look.
Alternatives comparison
Named competitors, point by point. Nobody paid to appear here or to be left out.
 Insomnia |  Cobalt |  Intruder |  Semgrep | |
|---|---|---|---|---|
| AI-driven autonomous exploitation | Yes — 7-agent AI red team with autonomous exploitation | No — human pentesters plus automated scanning | No — automated scanning with manual verification | No — static analysis only |
| Free tier / entry price | Free Community Edition; Advanced $149/mo | No free tier; per-engagement pricing | Free trial; paid plans from ~$100/mo | Free OSS tier; paid Semgrep AppSec Platform |
| SAST / source code analysis | Yes — free SAST CLI, 16+ languages, SARIF, IDE plugins | No — pentest-as-a-service focus | Limited — web app and infra scanning | Yes — core product, multi-language SAST |
| CI/CD integration | Yes — pipeline wizard, GitHub/GitLab/Jenkins export | Limited — engagement-based, not pipeline-native | Yes — CI/CD integrations available | Yes — first-class CI/CD and PR comments |
| Human pentesters included | No — AI agents only | Yes — core offering | Partial — manual verification add-on | No |
| Compliance attestations (SOC 2 / ISO) | Not found in collected content | Yes — SOC 2 and ISO 27001 published | Yes — ISO 27001 and SOC 2 | Yes — SOC 2 published |
Cobalt
Pentest as a Service platform that combines automated scanning with human pentesters.
Intruder
Automated security scanning platform focused on finding vulnerabilities in web apps and infrastructure.
Semgrep
Lightweight static analysis tool for finding bugs and enforcing code standards.
Comparing options? See Insomnia alternatives, scored side by side
More Security apps
View all Security
OBVELO
88Privacy gateway that masks personal data in LLM traffic

Sidenty
87Sidenty is a professional digital identity protection ser...

ProcessSpy
87A native macOS process explorer and advanced monitor that...

PromptTrace
85Free hands-on AI security labs for prompt injection and L...

Sanctix
85Sanctions screening with verifiable SHA-256 audit trails.

eGuard
84Verifiable parental controls for families in the Philippines

yourdrive
84YourDrive is a self-hosted file manager and media timeline that runs entirely on your own infrastructure. Organize files in nested folders, move them with drag-and-drop, search instantly, and browse photos and videos by month and year. Files stream straight to your own AWS S3, Azure Blob, MinIO, Cloudflare R2 or Wasabi storage. Install with one command. Free for personal use; teams pay per server, not per seat.

Noden
84Native macOS SSH, SFTP & RDP client with a Keychain-backe...

Archonum
84Real-device browser automation for AI agents

Privacy Requests
84DSAR management software for small teams.

VaultKeepR
84Password manager with no email, no account, no tracking. ...

PCDOTS Email Recovery Software
83Recovers emails from corrupt mailboxes across 50+ platforms.
A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.