Cycling through all six. Tap any point to stop.
Measured on six things
Sealed VMs for AI agents with instant rewind, audit trails & zero key exposureSealed VMs for AI agents with instant rewind and audit tr...
Growth
62Real, specific problem (agents with full host access) with a clear wedge against Docker, Firecracker, and E2B: local sealed VMs plus compliance. Regulated-enterprise angle is credible but the category is crowding fast.
Screenshots
1 / 3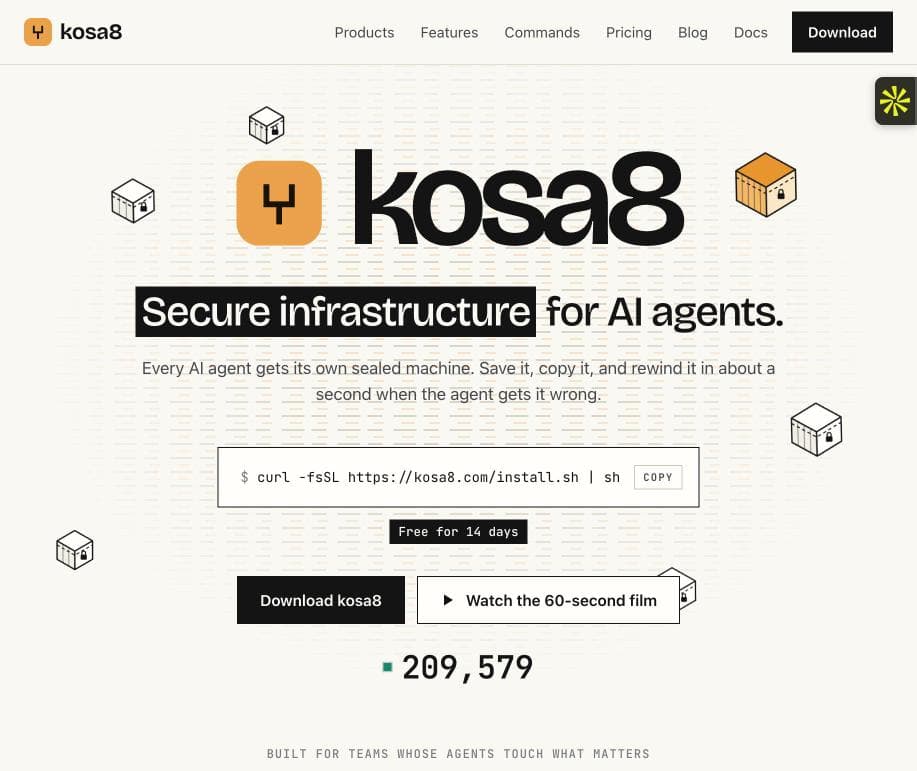
About this app
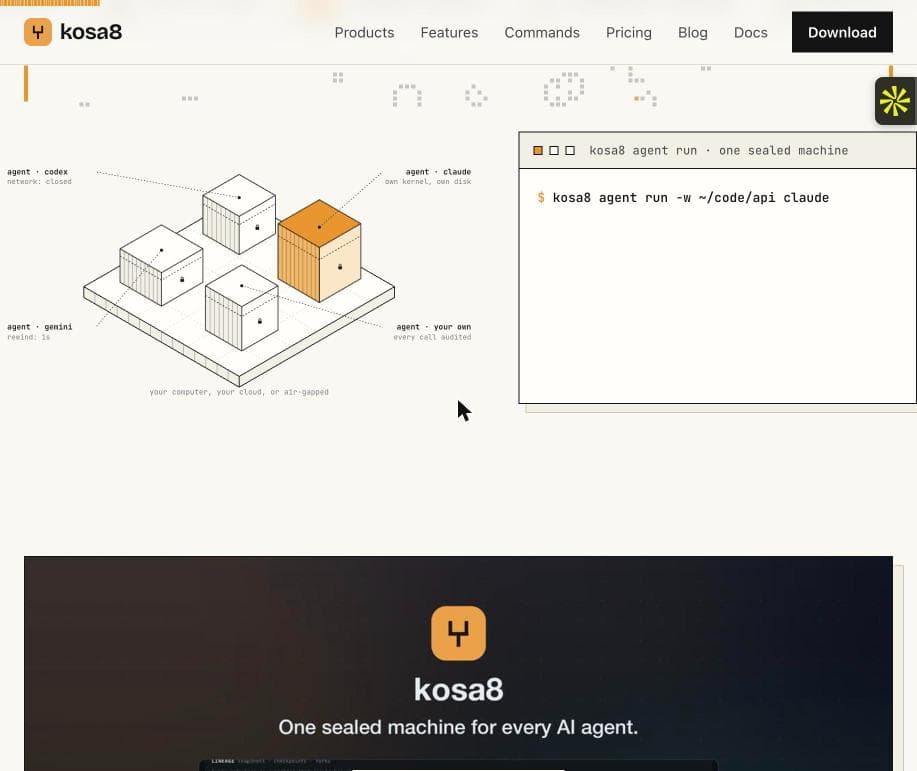
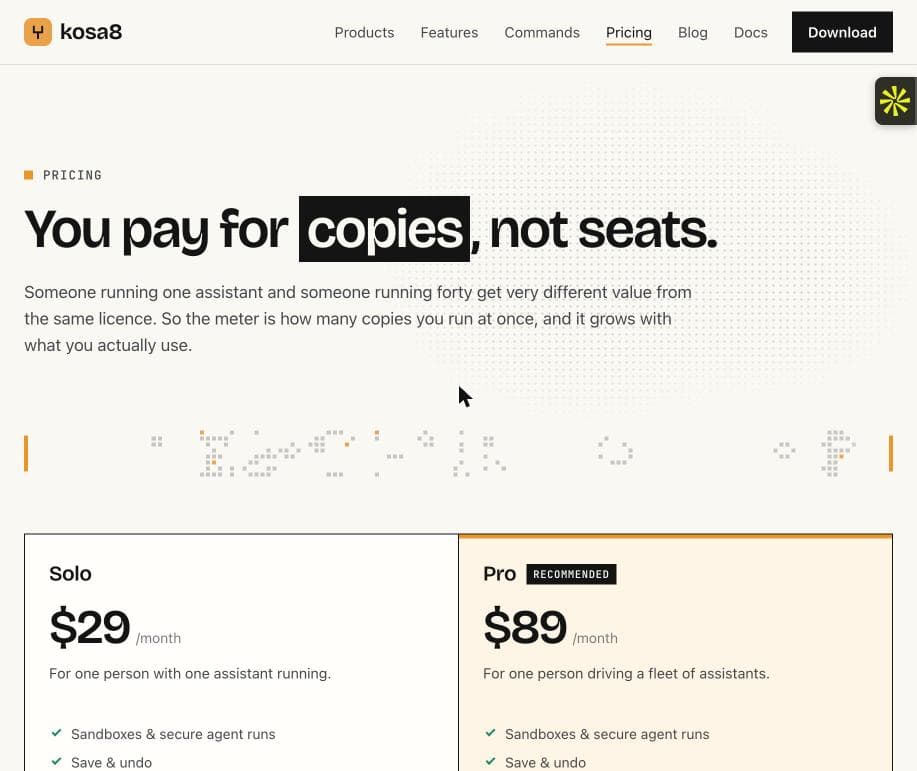
kosa8 is secure infrastructure that gives every AI agent its own sealed virtual machine. Think of it as a sandbox that's actually a full VM with its own kernel, not a shared container—so Claude Code, Codex, Gemini, or your own agents can run unattended without touching your keys, SSH credentials, or cloud secrets. Each sandbox sees only the folder you explicitly hand it, operates on a closed network with an allow-listed egress broker, and can be checkpointed and rewound in about a second when things go sideways. For teams, kosa8 adds hash-chained audit trails, two-person approvals for risky actions, signed org policies, FIPS 140-3 builds, and air-gapped operation. It speaks Docker (the CLI and Compose work unchanged), supports local models via an OpenAI/Anthropic-compatible API, and runs on Apple Silicon Macs, Linux, Windows 11 via WSL2, or fully air-gapped. Pricing starts at $29/month for solo use, with a 14-day free trial and no credit card required.
Key features
- 1Sealed full VM per AI agent with its own kernel, closed network, and allow-listed egress broker.
- 2One-second checkpoint and rewind; fork a running machine into multiple live copies.
- 3Docker-compatible CLI and Compose; local models via OpenAI/Anthropic-compatible API.
- 4Hash-chained audit trails, two-person approvals, signed org policies, FIPS 140-3 builds, air-gapped operation.
Target customer profile
Drawn from the product itself, not from a survey.
Demographic
Software teams and AI product developers
Pain points
Coding agents run with full shell, SSH keys, and cloud credentials—one poisoned package or prompt injection can reach everything.
Primary needs
Per-agent isolation, API key protection, closed network, and instant rollback when a run breaks something.
Demographic
Security operations and SOC teams
Pain points
Malware detonation requires disposable, faithful machines and a network it can't really reach; rebuilding training ranges takes hours.
Primary needs
Sealed VMs with simulated internet, signed detonation reports, and live clones for analyst training that reset on demand.
Demographic
Regulated enterprises (finance, health, government)
Pain points
Auditors ask what the AI did, who approved it, and where data went—most agent tools can't answer any of the three.
Primary needs
Hash-chained audit trails, two-person approvals, signed policies, FIPS 140-3 builds, and air-gapped operation.
Demographic
Founders and solo developers
Pain points
Wanting agents to work overnight but fearing one bad command could cost the laptop, keys, or weekend.
Primary needs
One-line install, checkpoint before risky steps, local models with no API bill, and free trial without a card.
Scout Review
Written by AI from measured evidence, scored out of 100.
kosa8 is a security-first sandbox for AI agents that takes its own pitch seriously: the site is fast, the headers are complete, and the copy doesn't waste words. The core idea — a real VM per agent with a closed network, key brokering, and one-second rewind — is a genuine differentiator against Docker's shared kernel and E2B's cloud-only model. The pricing structure (copies, not seats) is honest and well-explained. Where it falls short is depth of public proof: no docs site, no SOC 2 or pen-test evidence, no accessibility statement, and product claims that read as confident but unverified. For a tool asking regulated buyers to trust it, the receipts need to be as loud as the pitch.
Measure by measure
Usability
66One-line curl install, Docker-compatible CLI, and a no-card 14-day trial keep friction low for the target user. But no public docs or help center surfaced, and support routes through a single email address.
Design
74Dark, terminal-first aesthetic that fits the developer/security audience. Live CLI output as hero art is a smart, honest choice. Pricing page is clean and well-structured. Not visually distinctive beyond the category norm.
Speed
88Lighthouse mobile 96/100 (LCP 2.3s, CLS 0, TBT 36ms) and desktop 100/100. The marketing site is genuinely fast and lightweight. Product-side claims of 653ms sandbox boot are unverified but consistent with the pitch.
Security
80Full security header suite (HSTS, CSP, frame protection, Permissions-Policy), SPF and DMARC in place, 12/12 probe checks. Product claims hash-chained audits, two-person approval, and FIPS 140-3 builds — strong if true, but not independently verified.
Accessibility
78Lighthouse a11y 97/100, but two real failures: insufficient color contrast and visible text labels not matching accessible names. No WCAG statement or a11y documentation found. Solid automated baseline, fixable gaps.
Growth
62Real, specific problem (agents with full host access) with a clear wedge against Docker, Firecracker, and E2B: local sealed VMs plus compliance. Regulated-enterprise angle is credible but the category is crowding fast.
Improvement areas
- No public docs site or help center; support routes to a single email address.
- Compliance claims (FIPS 140-3, audit trails) lack public SOC 2 or pen-test evidence.
- Two Lighthouse accessibility failures: contrast ratios and accessible names.
- No public changelog, roadmap, or community presence to signal momentum.
Design & Usability
kosa8's site reads like it was built by people who actually use the product: the hero is live CLI output, the copy is blunt ('0 real keys inside the sandbox'), and the pricing page leads with a clear meter — copies, not seats. For a developer/security audience this lands well. Usability is where it thins out: the one-line curl install and Docker-compatible CLI are genuinely low-friction, and the no-card trial removes the usual signup tax, but there's no visible docs site, help center, or API reference in the fetched content. Support routes to a single email. For a product this technical, that's a gap — the target user will want to read before they run.
Speed & Security
Speed is the standout measured dimension: Lighthouse mobile 96/100 with LCP 2.3s and CLS 0, desktop a clean 100/100. The marketing site is lean and the terminal-style hero doesn't cost load time. Security is strong on the surface — full header suite, HSTS, CSP, SPF, DMARC, 12/12 probe checks — which is table stakes for a security product and kosa8 clears it. The product-level claims (hash-chained audit trails, two-person approval, FIPS 140-3 builds, air-gapped operation) are exactly what regulated buyers want to hear, but none of it is independently verifiable from public material. No SOC 2 report, no pen-test summary, no bug bounty page surfaced. For a tool asking banks and hospitals to trust it with agent credentials, that's the missing receipt.
Accessibility & Growth
Accessibility scores 97/100 on Lighthouse, but the two failing audits are real: insufficient color contrast and visible text labels not matching accessible names. On a dark-themed site aimed at technical users, contrast is the one that will actually bite. No WCAG conformance statement or accessibility documentation was found, which is normal for the stage but worth flagging. Growth is the more interesting question: kosa8 names a real, sharp problem — coding agents running with your shell, SSH keys, and cloud creds — and its wedge against Docker (shared kernel), Firecracker (DIY), and E2B (cloud-only) is coherent: local sealed VMs, instant rewind, and compliance features incumbents would have to become different companies to copy. The regulated-enterprise angle is credible but crowded, and the domain is only months old.
Conclusion
If you're a solo dev running Claude Code or Codex overnight and you've ever winced at what a bad command could do, kosa8 is aimed squarely at you and the 14-day no-card trial makes it cheap to find out. If you're a security team evaluating it for a bank or hospital, the header hygiene and compliance feature list are promising but you'll want to see the actual audit artifacts before signing anything. The product is early — domain registered months ago — and the site is more polished than the public documentation behind it. Worth a trial; not yet worth a procurement rubber stamp.
Suggestions for improvement
- Publish a real docs site with CLI reference, kit authoring guide, and troubleshooting — email-only support won't scale.
- Add a security page with SOC 2 status, pen-test summary, and a responsible-disclosure policy to back the FIPS and audit claims.
- Fix the two Lighthouse a11y failures: contrast ratios on the dark theme and accessible names on labeled controls.
- Ship a public changelog and roadmap so early adopters can see momentum and plan around it.
Alternatives comparison
Named competitors, point by point. Nobody paid to appear here or to be left out.
 kosa8 |  Docker |  Firecracker | E2B | |
|---|---|---|---|---|
| Isolation model | Full VM per agent with own kernel | Shared host kernel containers | MicroVM with VM-level isolation | Cloud sandbox, VM-level isolation |
| Local / air-gapped operation | Yes — local, air-gapped, FIPS builds | Local yes; air-gapped possible but no compliance layer | Self-hosted; requires significant setup | Cloud-only |
| Instant checkpoint / rewind | ~1s rewind; fork running machine into copies | Commit/snapshot, not instant rewind | Snapshot support, DIY orchestration | Fast startup; snapshot support varies |
| Audit trails & compliance | Hash-chained audits, 2-person approval, FIPS 140-3 | Enterprise add-ons; no agent-specific audit | None built-in | Limited; cloud-only compliance posture |
| Pricing entry point | $29/mo solo; 14-day free trial, no card | Free personal; paid team tiers | Free OSS; infra costs on you | Free tier; usage-based paid plans |
Docker
Container platform that shares the host kernel; faster than full VMs but offers weaker isolation and no built-in agent-specific security features like key brokering or instant rewind.
Firecracker
Open-source microVM technology from AWS that provides VM-level isolation, but requires significant setup and lacks kosa8's turnkey agent kits, audit trails, and policy enforcement.
E2B
Cloud sandbox for AI code execution with fast startup, but focuses on cloud-only operation rather than local, air-gapped, or regulatory-compliant deployments.
Comparing options? See kosa8 alternatives, scored side by side
More Security apps
View all Security
OBVELO
88Privacy gateway that masks personal data in LLM traffic

ProcessSpy
87A native macOS process explorer and advanced monitor that...

Sidenty
87Sidenty is a professional digital identity protection ser...

Basalt
86Eighteen PDF tools in one native Mac window: merge, split, compress, OCR, Bates numbering, forms, signing and redaction. Offline. $29 once.

Sanctix
85Sanctions screening with verifiable SHA-256 audit trails.

PromptTrace
85Free hands-on AI security labs for prompt injection and L...

eGuard
84Verifiable parental controls for families in the Philippines

yourdrive
84YourDrive is a self-hosted file manager and media timeline that runs entirely on your own infrastructure. Organize files in nested folders, move them with drag-and-drop, search instantly, and browse photos and videos by month and year. Files stream straight to your own AWS S3, Azure Blob, MinIO, Cloudflare R2 or Wasabi storage. Install with one command. Free for personal use; teams pay per server, not per seat.

Noden
84Native macOS SSH, SFTP & RDP client with a Keychain-backe...

Archonum
84Real-device browser automation for AI agents

VaultKeepR
84Password manager with no email, no account, no tracking. ...

Privacy Requests
84DSAR management software for small teams.
A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.