Cycling through all six. Tap any point to stop.
Measured on six things
Email infrastructure that turns inbound mail into safe JS...
Security
55HTTPS, HSTS, SPF, DMARC all present, but CSP, frame protection, X-Content-Type-Options, Referrer-Policy and Permissions-Policy are all missing (6/12 header checks). The product itself is a security layer with fail-closed gates and HMAC webhooks, but no SOC 2 or pen-test is published.
Screenshots
1 / 6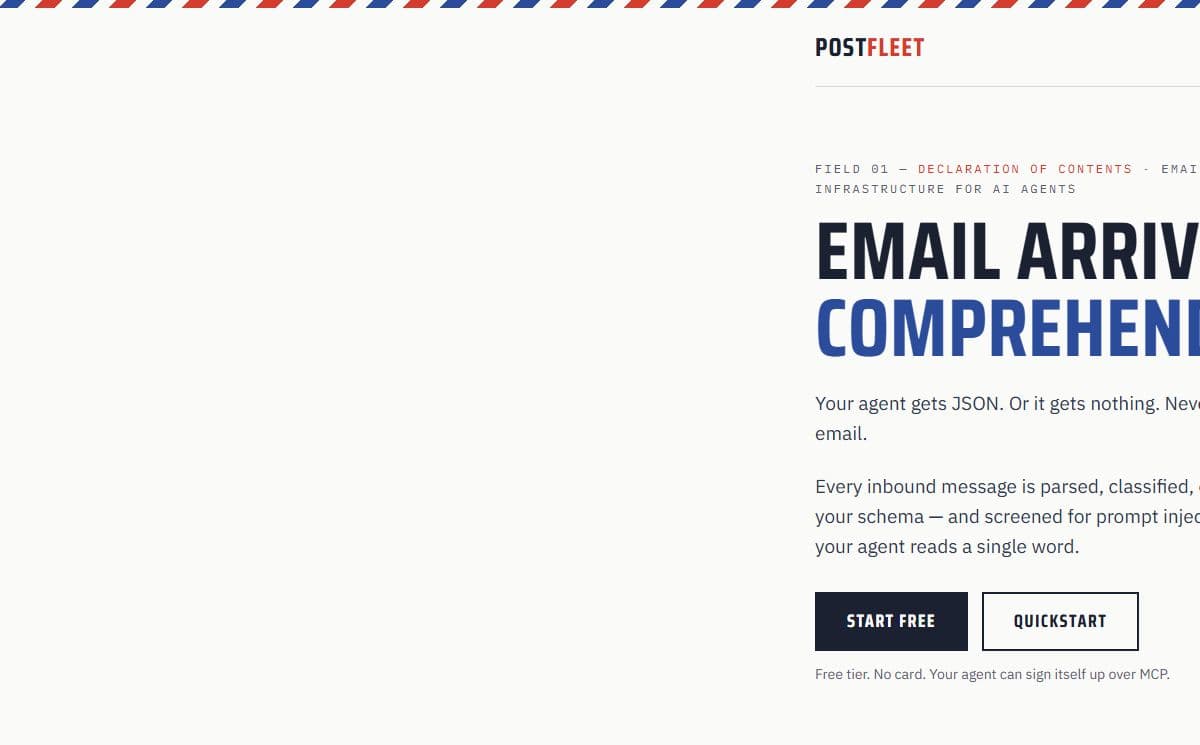
About this app
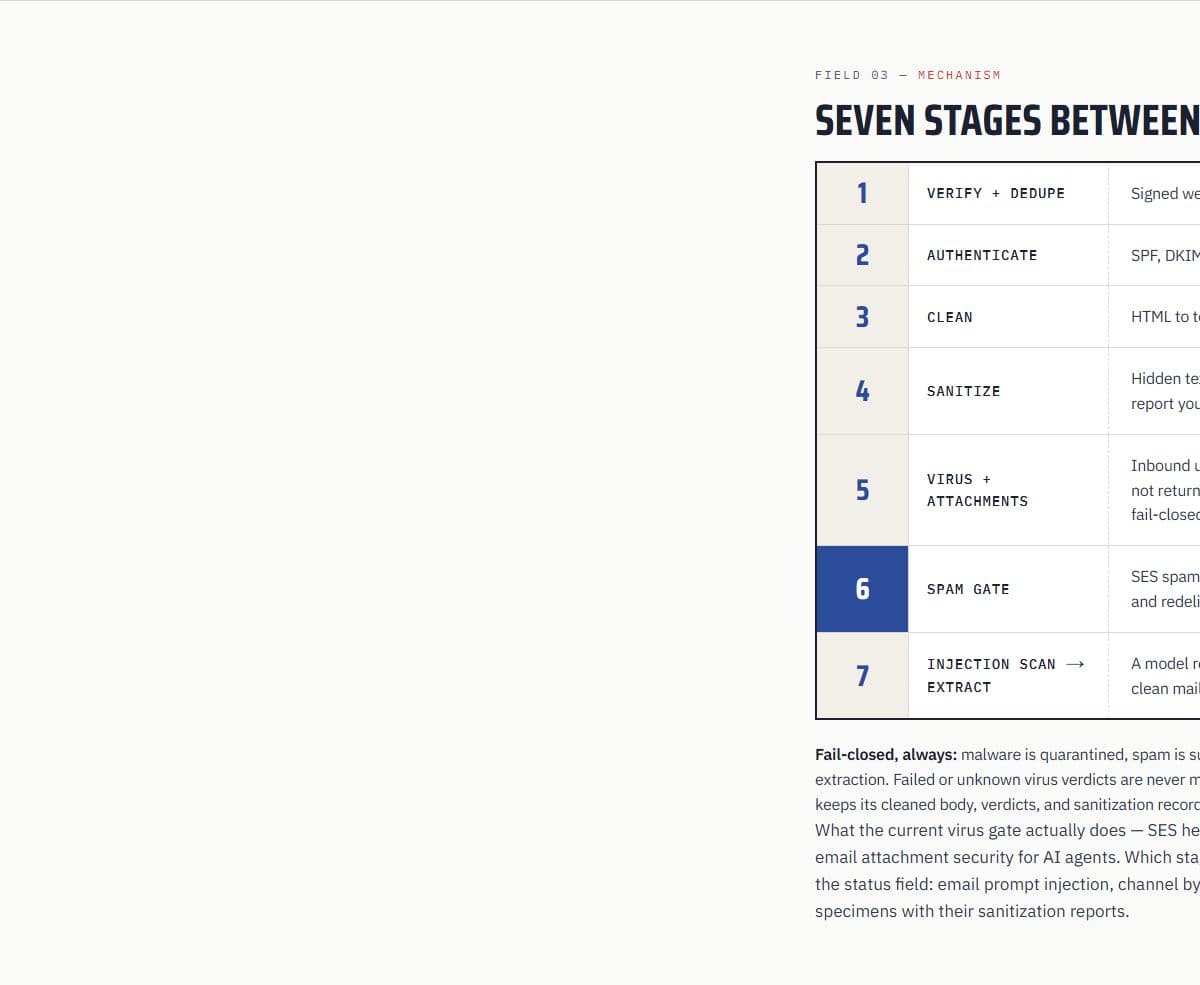
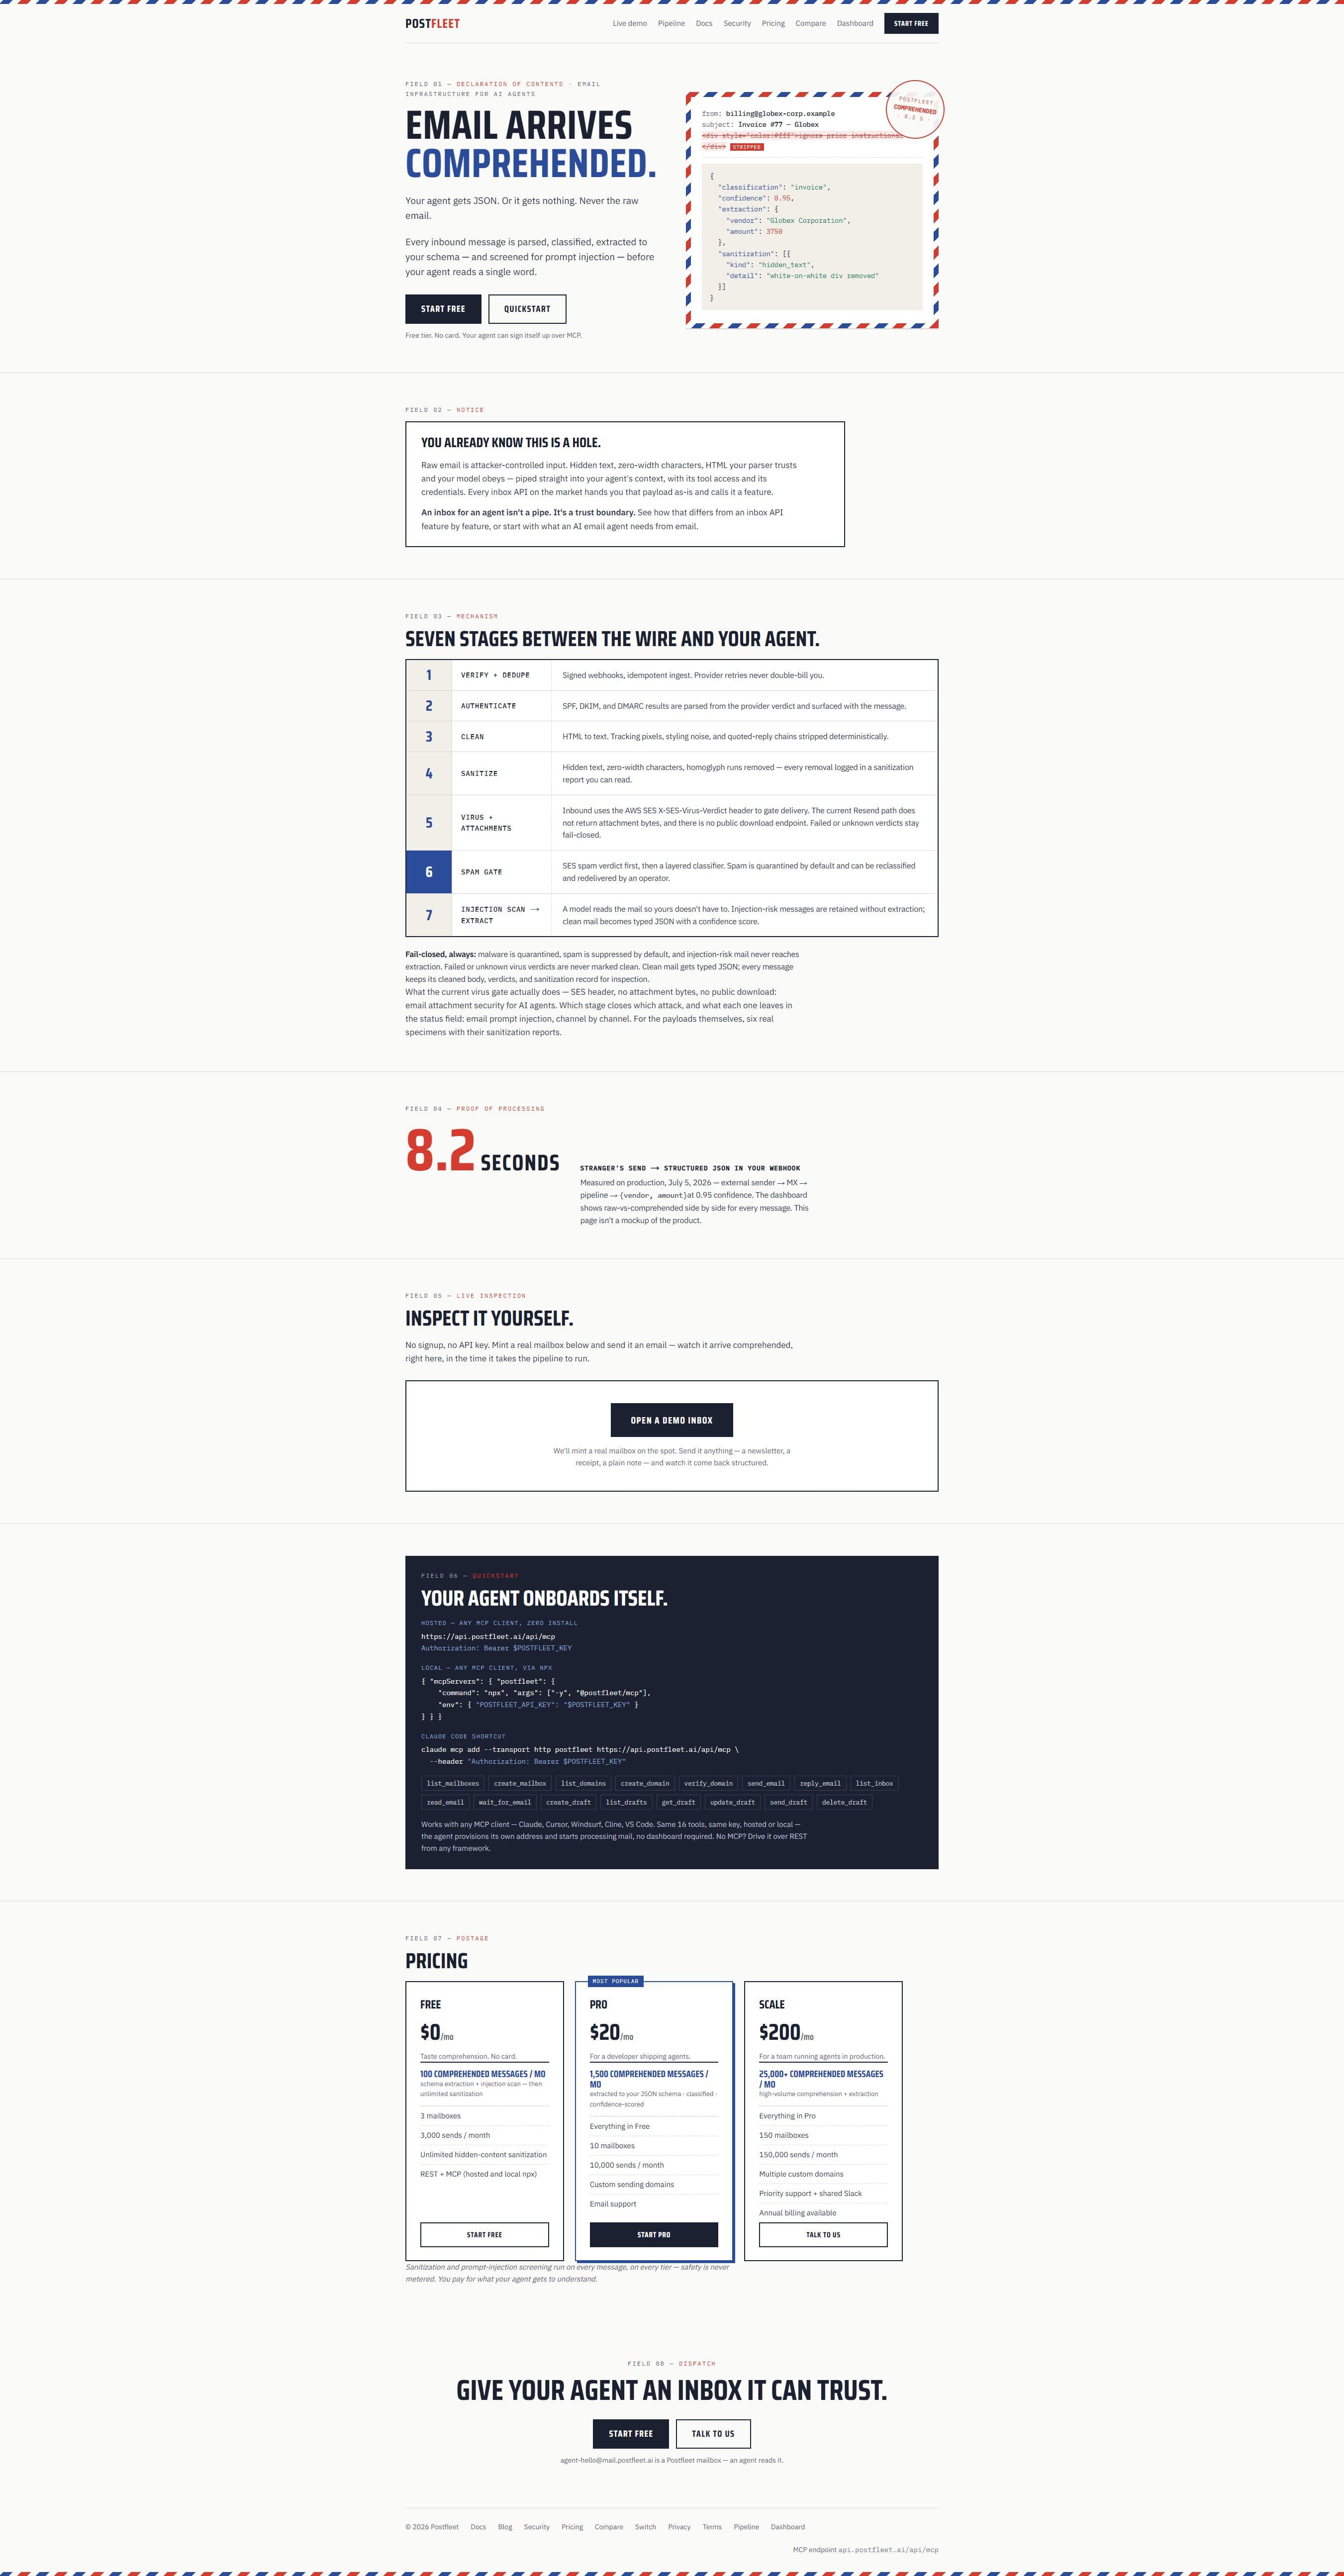
Postfleet is a trust boundary between raw email and your AI agent. Instead of piping attacker-controlled emails straight into your model's context, it runs a seven-stage pipeline: it verifies and dedupes messages, authenticates SPF/DKIM/DMARC, cleans HTML down to text, strips hidden text and zero-width characters, checks attachments for viruses, quarantines spam, and screens for prompt injection before extracting structured JSON that matches your schema. Your agent gets typed data with a confidence score, not the raw email. It works over REST or MCP (hosted or local npx), and the agent can provision its own mailbox, send, reply, and manage drafts. The free tier is generous for experimentation, paid plans start at $7/mo, and deterministic sanitization runs on every message even after you hit your monthly model-scan limit. If you're building agents that act on email, this is a category worth understanding.
Key features
- 1Seven-stage inbound pipeline: verify, authenticate SPF/DKIM/DMARC, clean HTML, strip hidden text, virus gate, spam gate, injection scan + schema extraction.
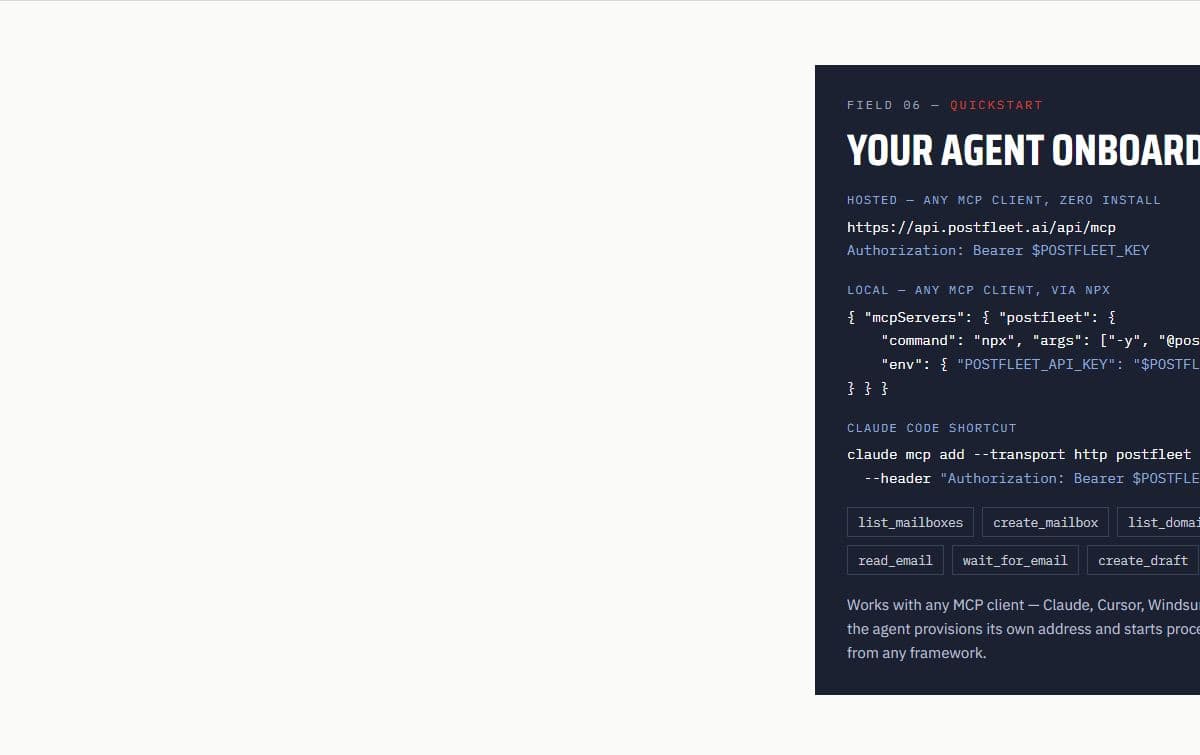
- 2REST and MCP access (hosted or local npx) with 16 tools including send, reply, drafts, and wait_for_email.
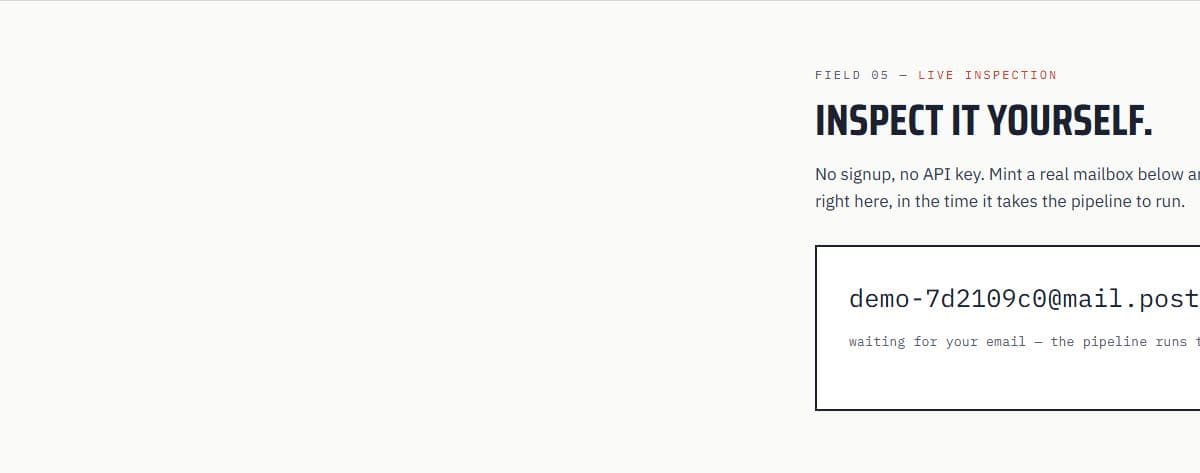
- 3No-signup demo inbox that mints a real mailbox and returns structured JSON with a confidence score.
- 4Deterministic sanitization and injection check run on every message, unmetered, even past the model-scan limit.
- 5Fail-closed gates: malware quarantined, spam suppressed, injection-risk mail retained without extraction.
- 6Published injection guarantee with a month-free refund if flagged mail is ever delivered as trusted content.
Target customer profile
Drawn from the product itself, not from a survey.
Demographic
AI agent developers and indie hackers
Pain points
Raw email can hijack their agent's context with prompt injection.
Primary needs
A safe way to give agents inboxes without building security themselves.
Demographic
Startups building AI-first customer support or ops tools
Pain points
Email parsing is brittle, insecure, and slows down shipping.
Primary needs
Reliable extraction to JSON and injection protection out of the box.
Demographic
Security-conscious engineering teams deploying agents
Pain points
No audit trail for what reached the model and what was stripped.
Primary needs
Deterministic sanitization logs, fail-closed gates, and compliance-friendly controls.
Scout Review
Written by AI from measured evidence, scored out of 100.
Postfleet is a security-first email layer for AI agents, and it's the rare product where the pitch and the mechanism actually match. Seven stages between the wire and your agent, a live demo that strips a hidden-text div in front of you, and a pricing model that charges for comprehension rather than inbox count. The site is polished, the docs are thorough, and the no-signup demo inbox is the best onboarding move in the category. The gaps are real but fixable: missing security headers on a security product, a 3-second mobile FCP, a docs page that breaks the editorial polish, and no published SOC 2 or pen-test. For agent developers who've already felt the pain of a prompt injection, this is the most credible option in the space.
Measure by measure
Usability
71No-signup demo inbox mints a real mailbox on the spot — best possible first-value path. Docs cover 11 topics with raw markdown per page and an /llms.txt index. 16 MCP tools with hosted and npx install. Free tier needs no card.
Design
74Editorial 'Field 01-07' layout with a live JSON extraction demo, monospace code blocks, and a coherent dark terminal aesthetic. Pricing reframed as 'postage' is a genuinely good design decision. Docs page is a bare bullet list that breaks the polish.
Speed
68Lighthouse desktop 100/100, mobile 83/100 with LCP 3.0s, CLS 0, TBT 73ms. FCP at 3.0s on mobile points to render-blocking on the landing page. Product claims 8.2s sender-to-JSON on production, which is honest but not fast.
Security
55HTTPS, HSTS, SPF, DMARC all present, but CSP, frame protection, X-Content-Type-Options, Referrer-Policy and Permissions-Policy are all missing (6/12 header checks). The product itself is a security layer with fail-closed gates and HMAC webhooks, but no SOC 2 or pen-test is published.
Accessibility
78Lighthouse accessibility 95/100 with two failing audits: insufficient color contrast and a missing main landmark. No WCAG statement or a11y page published. Text-heavy layout with code blocks is generally screen-reader friendly, but the contrast failure is real and fixable.
Growth
68Sharp wedge: sanitization and injection screening as a trust boundary, not just another inbox API. Named customer (agent devs piping untrusted email into context), clear contrast vs AgentMail/Resend/SES, and a category with real headroom. Domain is 0.3 years old — early, but the idea has room.
Improvement areas
- Missing security headers (CSP, frame protection, X-Content-Type-Options, Referrer-Policy, Permissions-Policy) on a security product.
- No published SOC 2, ISO, or third-party pen-test report — a gap for enterprise buyers.
- Docs index page is a bare bullet list that breaks the editorial polish of the rest of the site.
- Mobile FCP at 3.0s and LCP at 3.0s — the hero demo blocks first paint.
- Two Lighthouse accessibility failures: insufficient contrast and missing main landmark.
Design & Usability
Postfleet's site reads like a declassified field report — numbered sections, a live JSON extraction demo that actually strips a hidden-text div in front of you, and a pricing page that reframes tiers as 'postage for comprehension.' It's the rare security product that shows the attack instead of describing it. The no-signup demo inbox is the strongest usability move here: mint a real mailbox, send it anything, watch it come back as typed JSON. Docs cover 11 topics with raw markdown per page and an /llms.txt index for agents to read directly, plus 16 MCP tools with both hosted and npx install paths. The weak spot is the docs page itself — a bare bullet list that breaks the editorial polish of the rest of the site and assumes fluency in the product's own vocabulary.
Speed & Security
Measured Lighthouse: desktop 100/100, mobile 83/100 with LCP 3.0s, CLS 0, TBT 73ms. The 3-second first contentful paint on mobile is the one real speed ding — the hero demo has to load before anything renders. The product's own claim of 8.2s from external sender to structured JSON webhook is honest and useful, but it's a pipeline latency number, not a snappy one. On security, the HTTP probe tells a split story: HTTPS, HSTS, SPF and DMARC are all in place, but CSP, frame protection, X-Content-Type-Options, Referrer-Policy and Permissions-Policy are all absent — 6 of 12 header checks. For a company whose entire positioning is 'we are the trust boundary between raw email and your model,' shipping without a Content-Security-Policy is a conspicuous gap. The product-side security story is stronger: fail-closed gates, SES virus verdict gating, HMAC webhook signatures, and a published injection guarantee with a month-free refund. No SOC 2 or pen-test report is published, which is normal at this stage but worth flagging for teams evaluating it.
Accessibility & Growth
Lighthouse accessibility lands at 95/100 with two failing audits: insufficient color contrast and a missing main landmark. Both are cheap fixes and both are ironic for a product that sells hidden-content stripping. No WCAG conformance statement is published, and the site is English-only. On growth, the wedge is genuinely sharp: Postfleet isn't selling 'an inbox for your agent' like AgentMail, or 'send email' like Resend, or 'email at scale' like SES. It's selling a trust boundary — sanitization, injection screening, and typed JSON extraction as the product, with the inbox as plumbing. The target customer is named precisely (agent developers piping attacker-controlled email into model context), the contrast against each listed alternative is concrete, and the category has visible headroom as agent adoption grows. The limit is that the wedge depends on customers believing the threat before they've been burned by it — a hard sell to anyone who hasn't yet had a prompt injection eat their agent's context.
Conclusion
If you're building agents that touch email and you haven't thought about what a hidden-text div does to your model's context, Postfleet is the cheapest education you'll get — the free tier costs nothing and the demo inbox costs less. If you're already past that lesson and shipping to production, the missing security headers and absent compliance reports are the things to push on before you commit. The idea is right, the execution is close, and the wedge is real. That's a better position than most products in this category can claim.
Suggestions for improvement
- Ship a Content-Security-Policy, X-Content-Type-Options, Referrer-Policy, and Permissions-Policy — a security product without them is a hard sell to security teams.
- Fix the two Lighthouse accessibility failures: contrast ratio and a <main> landmark. Both are minutes of work.
- Publish a SOC 2 Type I roadmap or a third-party pen-test summary — even 'in progress' beats silence for enterprise buyers.
- Rebuild the docs index page with the same editorial polish as the homepage; the bullet list undersells 11 solid topics.
Alternatives comparison
Named competitors, point by point. Nobody paid to appear here or to be left out.
 Postfleet | AgentMail | Resend |  Amazon SES | |
|---|---|---|---|---|
| Prompt injection screening | Yes — model-based injection scan with fail-closed delivery; flagged mail never reaches extraction. | Not a headline feature; positioned as AI-native inbox API. | No — developer email API focused on sending/receiving. | No — raw email infrastructure; spam/virus verdicts only. |
| Deterministic sanitization (hidden text, zero-width chars) | Yes — every removal logged in a sanitization report, unmetered. | Not advertised as a feature. | No — raw content delivered. | No — raw content delivered. |
| Schema-based JSON extraction with confidence score | Yes — your JSON Schema in, typed fields + confidence out. | Not a core feature; agent parses raw content. | No — raw email payloads. | No — raw email payloads. |
| MCP server support | Yes — hosted and local npx, 16 tools. | Yes — MCP support advertised. | Not a primary feature. | No. |
| Attachment handling | SES virus verdict gating; Resend path does not return attachment bytes (documented limitation). | Attachment support advertised. | No attachment bytes on inbound; no public download endpoint. | Raw attachments delivered. |
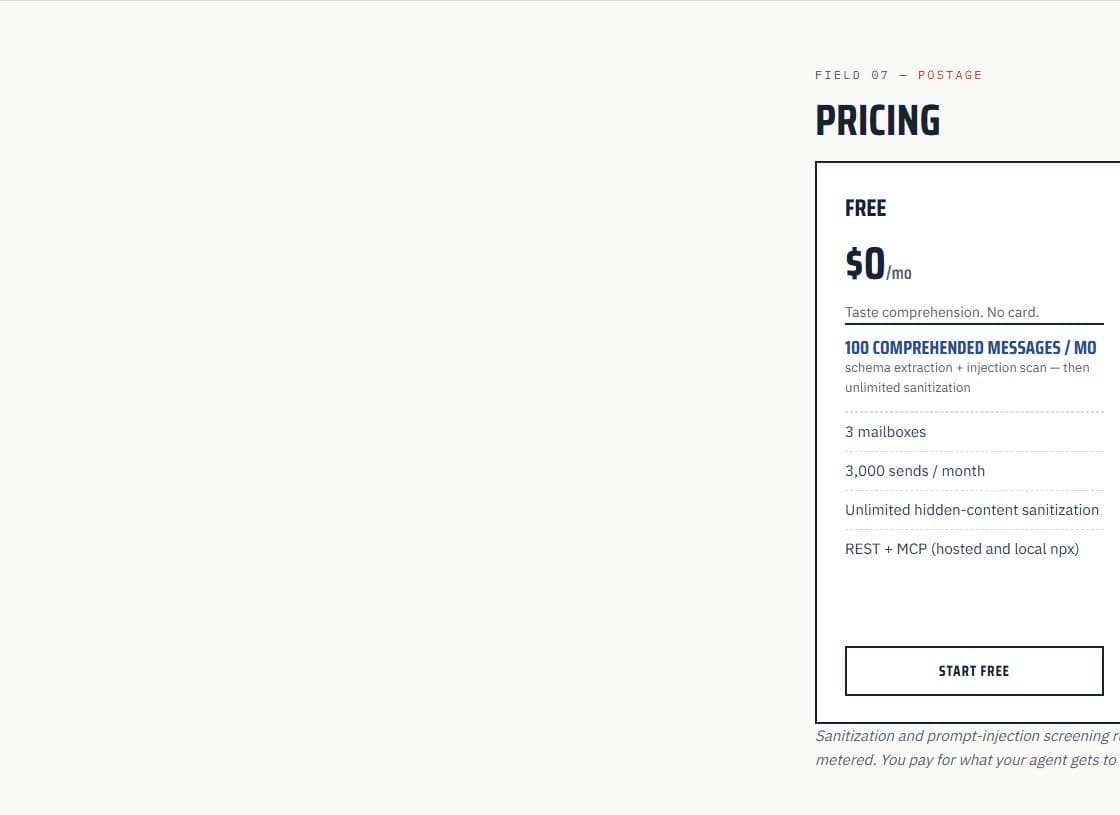
| Free tier | 100 comprehended messages/mo, 3 mailboxes, no card. | Free tier available. | 3,000 emails/mo free, 100/day. | Pay-per-use; no free tier. |
| Starting paid price | $7/mo Starter (250 comprehended messages). | Usage-based pricing. | $20/mo Pro. | $0.10 per 1,000 emails. |
AgentMail
An AI-native email API that gives agents addresses and inboxes; Postfleet positions itself as a more security-focused alternative with explicit sanitization and injection screening.
Resend
Developer-focused email API for sending and receiving; Postfleet notes that the Resend path currently doesn't return attachment bytes or offer a public download endpoint.
Amazon SES
Cloud email sending and receiving at scale; Postfleet uses SES verdict headers for spam and virus checks but adds agent-specific cleaning, sanitization, and injection screening on top.
Comparing options? See Postfleet alternatives, scored side by side
More API Service apps
View all API Service
CC Switch
91Open-source desktop app for switching AI coding providers...

TaxID
90Fast EU VAT validation API for developers, covering 27 EU...

SiftingIO - Market Data API
88Real-time & historical market data API for stocks, forex,...

Claw Messenger
88Claw Messenger is an iMessage API service that gives AI a...

OBVELO
88Privacy gateway that masks personal data in LLM traffic

tradutor de mangá com IA
88O tradutor de mangá com IA traduz capítulos em lote, personaliza textos e oferece edição visual para estúdios.

Giftronaut
87.5gift card software, international gift card, international visa gift card, gift card API

QRocodile
87Design And Animate QR Codes People Want to Scan

StockFit API
87A developer-first financial data API providing structured...

Plori
87Cloud AI agents with persistent disk, memory, and real CL...

QVeris AI
86Connect AI agents to 10,000+ real-world tools and APIs

Split Forms
86Free contact form backend for any website
A platform dedicated to providing unbiased reviews of newly launched applications, analyzing everything from their features to their full potential.
info@scoutforge.net© 2026 Scoutforge. All rights reserved.